
Active Directory Penetration Testing: Finding the Risks Hidden Inside Your Domain
Active Directory penetration testing identifies attack paths involving credentials, excessive privileges, misconfiguration and lateral movement.
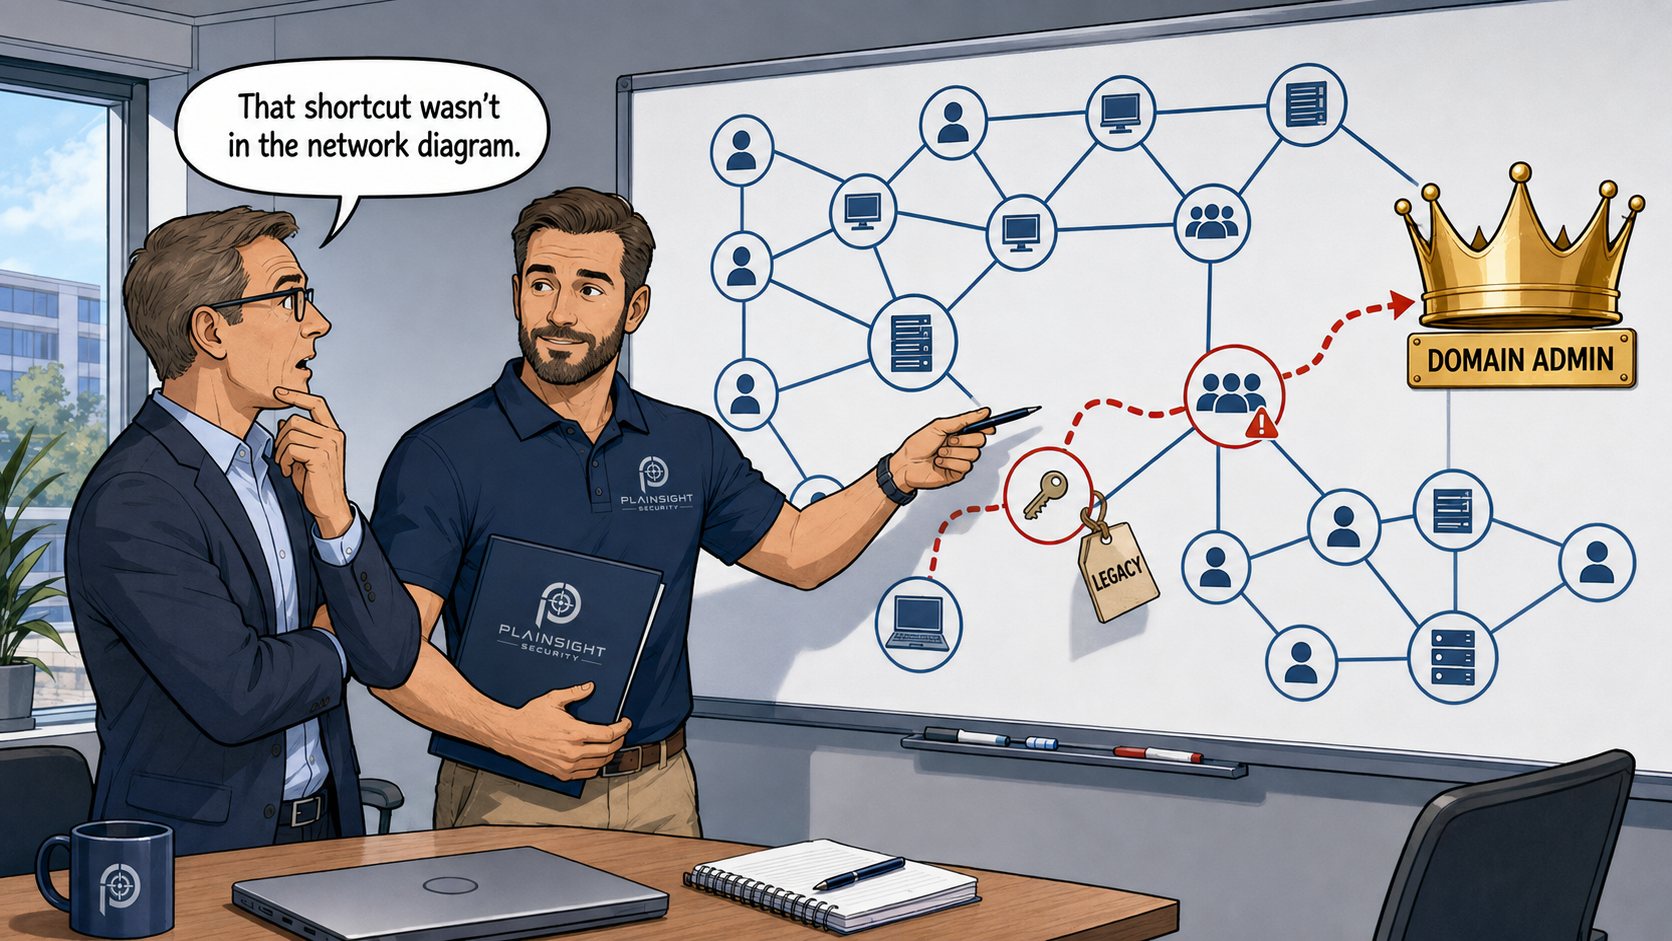
Active Directory is at the heart of the IT environment for many organisations. It manages users, computers, authentication and access to critical resources, making it an attractive target for attackers.
An Active Directory penetration test is an authorised security assessment that examines whether weaknesses in an organisation's Windows domain could allow an attacker to gain unauthorised access, escalate privileges, move between systems or ultimately compromise the domain.
Unlike a simple vulnerability scan, Active Directory penetration testing looks at how individual weaknesses can be combined to create a realistic attack path.
Why Does Active Directory Need Penetration Testing?
Active Directory can become extremely complex over time.
Users, computers, groups, service accounts, permissions and policies are continually added and changed. Legacy configurations may remain in place long after their original purpose has disappeared.
A domain can therefore contain security weaknesses that are difficult to identify through conventional vulnerability scanning.
For example, an attacker might be able to:
- Obtain valid credentials through password spraying
- Extract or crack service account credentials
- Abuse excessive permissions
- Exploit weaknesses in NTLM authentication
- Take advantage of insecure delegation
- Compromise a privileged account
- Move laterally between systems
- Escalate privileges within the domain
- Ultimately obtain Domain Administrator or equivalent control
The individual weaknesses may appear relatively minor. When combined, however, they can result in complete domain compromise.
What Is Tested During an Active Directory Penetration Test?
An Active Directory penetration test typically examines the security of the domain from the perspective of an attacker who has obtained an initial foothold.
The exact scope depends on the engagement, but testing can include authentication, privilege management, domain configuration, credential exposure, permissions and opportunities for lateral movement.
User and Account Security
Testers examine how user accounts are protected and whether weaknesses could allow credentials to be obtained or abused.
This can include looking for:
- Weak or predictable passwords
- Password spraying opportunities
- Excessive account privileges
- Insecure service accounts
- Stale or unnecessary accounts
- Accounts with dangerous administrative rights
- Exposed credentials
- Inappropriate group membership
The objective is not simply to identify weak passwords, but to understand what an attacker could achieve after compromising an account.
Password Spraying
Password spraying is an attack technique where a small number of commonly used passwords are tested against many accounts rather than repeatedly attempting passwords against a single account.
This can sometimes bypass account lockout policies that would otherwise prevent traditional brute-force attacks.
During an authorised penetration test, password spraying can help determine whether the organisation's authentication controls provide adequate protection against this type of attack.
Testing should be carefully controlled to minimise the risk of account lockouts or disruption.
Kerberoasting
Kerberoasting is a technique that can allow an attacker with domain credentials to request service tickets for accounts associated with services.
Depending on how service accounts are configured, the resulting tickets may be susceptible to offline password cracking.
If a compromised service account has significant privileges, this can provide an attacker with a path towards further privilege escalation.
Testing for Kerberoasting therefore considers both the technical configuration and the potential impact of compromised service accounts.
NTLM and Credential Exposure
NTLM is an older Windows authentication protocol that remains present in many environments.
Where NTLM is still enabled, attackers may be able to exploit weaknesses involving authentication, credential relay or credential capture, depending on the wider environment.
An Active Directory penetration test can assess where NTLM is being used and whether its configuration creates opportunities for an attacker.
This is particularly important in environments that have evolved over many years and still contain legacy systems or applications that depend on older authentication mechanisms.
Delegation and Privilege Escalation
Active Directory delegation can provide legitimate functionality, but insecure configurations can introduce significant security risks.
Testing can examine delegation relationships and identify situations where an attacker could abuse them to obtain additional privileges.
Privilege escalation may also involve:
- Excessive group memberships
- Misconfigured access control lists
- Weak service permissions
- Dangerous rights assigned to users or groups
- Misconfigured computer accounts
- Credential exposure
- Poorly secured administrative interfaces
The goal is to determine whether a low-privileged account can be turned into a significantly more powerful account.
ACL Abuse
Access Control Lists (ACLs) determine who can perform actions against objects within Active Directory.
ACL misconfigurations can sometimes give users or groups more control than intended.
For example, an account might have permissions that allow it to modify another account, change group membership or alter an object that ultimately provides a path to higher privileges.
These relationships can be difficult to spot manually because the problem may not be the permission itself, but what that permission allows an attacker to do when combined with other permissions.
Lateral Movement
Once an attacker compromises one system or account, they will often attempt to move further into the environment.
An Active Directory penetration test can assess whether compromised credentials or systems provide opportunities to access additional machines.
This may involve examining:
- Administrative access between workstations and servers
- Reused credentials
- Remote management services
- Stored credentials
- Local administrator privileges
- Server and workstation trust relationships
- Access to sensitive systems
The objective is to understand whether an attacker who compromises one endpoint could use it as a stepping stone towards more valuable systems.
Domain Compromise
The ultimate objective of many Active Directory attacks is to obtain control of the domain.
Domain compromise can provide an attacker with extensive access to users, computers, servers and business resources.
A penetration test therefore looks beyond individual vulnerabilities and considers the complete attack path.
For example:
Initial access → credential compromise → privilege escalation → lateral movement → privileged account → domain compromise
A good penetration test demonstrates whether such an attack path is realistically achievable and identifies the controls that could prevent it.
Why Vulnerability Scanning Isn't Enough
Vulnerability scanners are valuable tools, but they cannot replace Active Directory penetration testing.
A vulnerability scanner might identify an outdated operating system, a missing patch or a known vulnerability.
It is much less likely to answer questions such as:
If an attacker compromises this account, what can they access?
Or:
Can these apparently minor permissions be chained together to obtain administrative control of the domain?
Penetration testing provides the human-led assessment required to understand these relationships.
What Happens During an Active Directory Penetration Test?
The exact methodology varies depending on the scope and objectives of the engagement, but a typical assessment may include:
1. Reconnaissance
The tester establishes an understanding of the Active Directory environment, including domains, users, groups, computers and relevant services.
2. Initial Access
Where appropriate to the agreed scope, the tester assesses whether an attacker could obtain or abuse valid credentials or otherwise gain an initial foothold.
3. Enumeration
The environment is examined to identify relationships, permissions, trusts, administrative access and potential attack paths.
4. Exploitation
Identified weaknesses are safely tested to determine whether they can actually be exploited.
5. Privilege Escalation
The tester assesses whether access can be escalated from a low-privileged account towards higher levels of access.
6. Lateral Movement
The assessment examines whether compromised accounts or systems can be used to reach additional systems.
7. Domain-Level Impact
Where permitted by the rules of engagement, the tester determines whether the identified attack path could result in domain compromise.
8. Reporting and Remediation
The findings are documented with their security impact, evidence and practical recommendations for remediation.
What Makes Active Directory Testing Different From a Standard Internal Penetration Test?
There is considerable overlap between internal infrastructure penetration testing and Active Directory penetration testing.
However, Active Directory testing places particular emphasis on the identity and trust relationships that underpin the Windows environment.
The tester is not simply looking for vulnerable servers.
They are examining how users, groups, computers, permissions, authentication mechanisms and trust relationships interact.
This is important because an organisation may have fully patched servers and still have a serious Active Directory security problem.
Who Should Consider Active Directory Penetration Testing?
Active Directory penetration testing can be valuable for organisations that use Microsoft Active Directory to manage their Windows environment.
It is particularly relevant for organisations that:
- Store sensitive or commercially valuable information
- Have large or complex Windows environments
- Have multiple sites or offices
- Have acquired or merged with other organisations
- Have legacy Active Directory configurations
- Have experienced significant staff or administrator changes
- Need assurance over privileged access
- Are preparing for regulatory or customer security requirements
- Want to understand the potential impact of a compromised workstation or user account
It can also be particularly valuable for organisations with on-premises Active Directory, where legacy configurations and long-established trust relationships may present risks that are not immediately apparent.
How Often Should Active Directory Be Tested?
There is no single frequency that is appropriate for every organisation.
Testing should take into account factors such as the size and complexity of the environment, the sensitivity of the information being protected and the frequency of significant infrastructure changes.
An assessment should also be considered following major changes such as:
- Active Directory migrations
- Domain consolidation
- Acquisitions or mergers
- Major infrastructure changes
- Changes to privileged access
- Introduction of new authentication technologies
- Significant security incidents
Regular testing provides greater assurance because Active Directory is not static. New users, computers, applications and permissions are continually introduced.
Active Directory Security Is About Attack Paths, Not Just Vulnerabilities
One of the most important benefits of Active Directory penetration testing is that it provides an attacker-focused view of the environment.
A single configuration issue may not represent a serious vulnerability in isolation.
But if that issue allows an attacker to compromise an account, that account provides access to another machine, and that machine exposes credentials that lead to a privileged account, the combined risk can be substantial.
Penetration testing helps organisations understand these relationships.
Instead of simply asking:
"What vulnerabilities do we have?"
the more important question becomes:
"What could an attacker actually do with them?"
Conclusion
Active Directory remains a critical component of many business IT environments, and compromising it can give an attacker extensive control over an organisation's systems and data.
Active Directory penetration testing provides a practical way to assess whether weaknesses in authentication, permissions, delegation, credential management and configuration can be combined into a realistic path to privilege escalation and domain compromise.
For organisations relying on on-premises Active Directory, particularly those with long-established or complex environments, an independent penetration test can provide valuable insight into risks that automated vulnerability scanning may not identify.
The objective is not simply to find vulnerabilities. It is to understand how an attacker could move through the environment, what they could ultimately access, and what can be done to stop them.
For more information about Active Directory and internal infrastructure security testing, contact Plainsight Security to discuss your requirements.

Written by
Mark Tomlinson
Our lead penetration tester, Mark Tomlinson, holds The Cyber Scheme Team Leader qualification in infrastructure penetration testing, an advanced certification recognised by the National Cyber Security Centre (NCSC) and used by professionals testing government systems and UK critical national infrastructure. Mark is also registered with the UK Cyber Security Council as a Principal Cyber Security Professional (PriCSP) specialising in Security Testing and holds an MSc in Computer Science with Cyber Security.
More about how we workPut this into practice.
Cyber Essentials, Cyber Essentials Plus, and penetration testing — fixed-price, plain English, and built to stay out of your way.