Active Directory attack paths
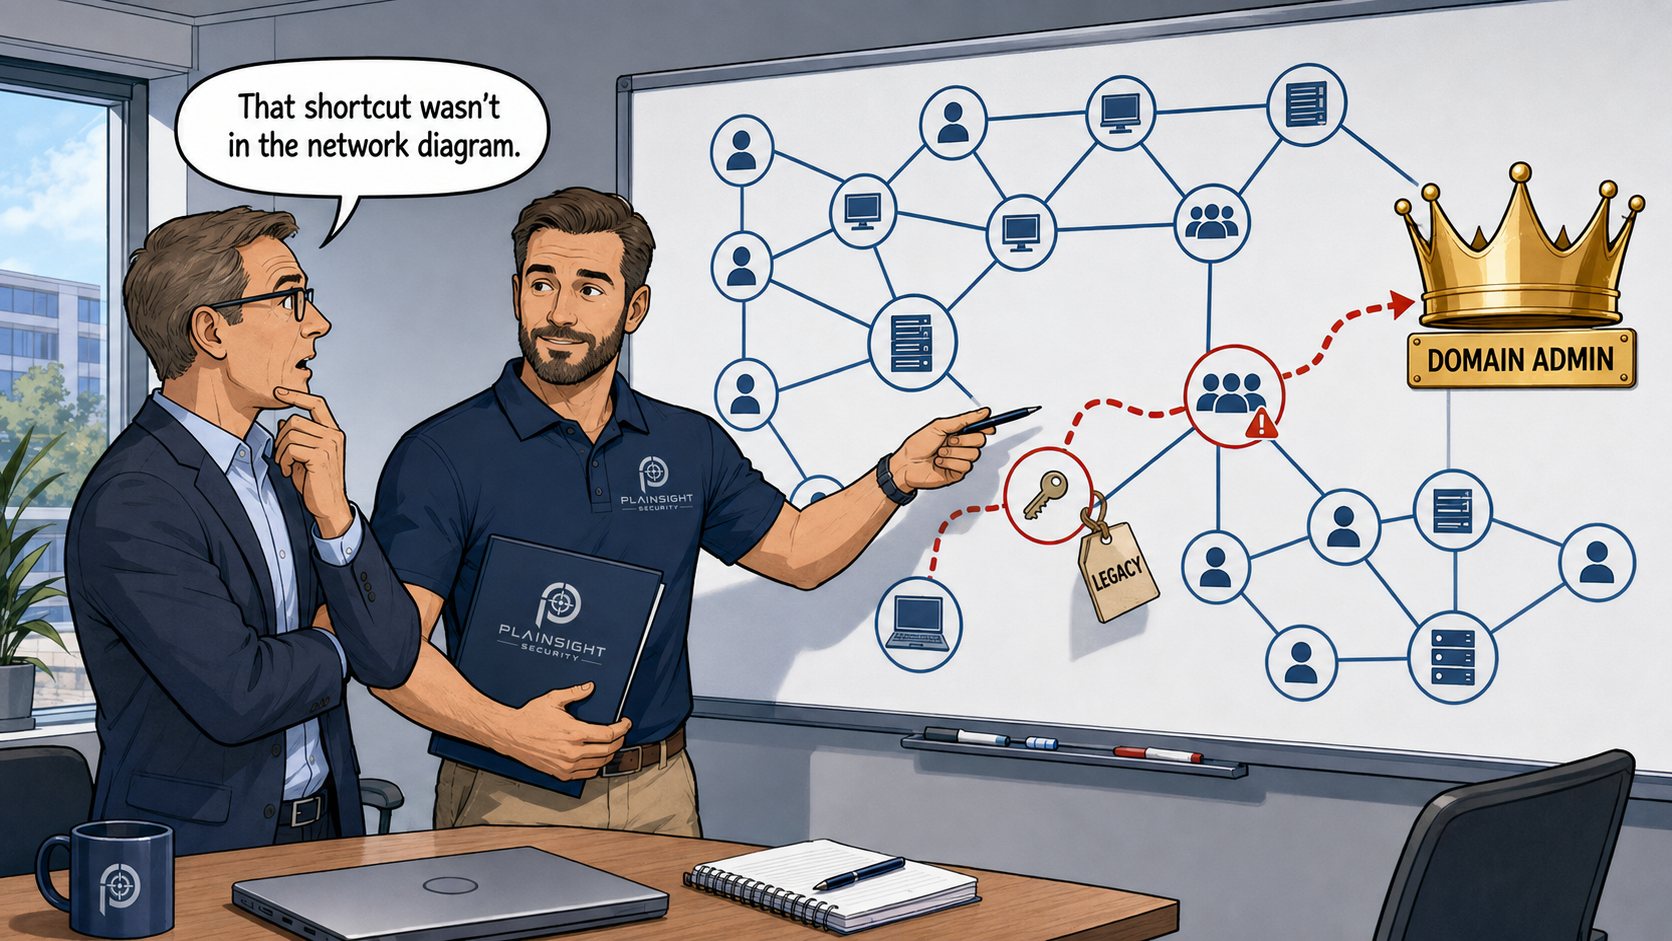
The misconfigurations and weaknesses that let an attacker climb from an ordinary account to domain-wide control, including weak Kerberos settings, over-privileged accounts and well-known escalation paths.

Find out what an attacker could do once they're inside.
Assume-breach testing from within your network, including Active Directory, delivered to a recognised methodology by a Cyber Scheme Team Leader qualified tester.
Perimeters get bypassed. Someone clicks a phishing link, a laptop is lost, a contractor plugs in a device. The damage is decided by what an attacker can do next, once they already have a foothold inside.
We test from that starting point. Given a normal position on your network, we see how far an attacker could move, whether they could escalate from an ordinary user to domain-wide control, and what sensitive data or systems they could reach. Then we give you a prioritised list of the paths to close first.
The misconfigurations and weaknesses that let an attacker climb from an ordinary account to domain-wide control, including weak Kerberos settings, over-privileged accounts and well-known escalation paths.
How far a foothold spreads: moving between systems, escalating privileges, and turning a single compromised device into control of many.
Passwords and tokens cached, reused or left in the open, and how an attacker would gather and reuse them across your estate.
Whether the boundaries between your networks actually hold, or whether a foothold in one area quietly reaches everything else.
Unpatched internal systems and weakly configured services that a scanner outside your perimeter would never see.
File shares and internal stores holding sensitive data that far more people can reach than should, a common and quiet source of exposure.
Infrastructure testing is delivered to a recognised methodology by a tester holding The Cyber Scheme's Team Leader qualification for infrastructure testing, which is recognised by the NCSC against UK government testing standards. Our lead tester is also a UK Cyber Security Council registered Principal (PriCSP) for Security Testing.
In practice that means industry-standard tooling for breadth, then manual testing and the chaining of issues to work out what an attacker could really achieve inside your network, and a report you can act on.
A short enquiry, answered by a tester rather than a sales team.
15 to 30 minutes on your estate, your sites, and whether Active Directory is in scope.
Clear scope, clear price, clear dates, typically within 48 hours.
Agreed rules of engagement, testing to a recognised methodology, then a report you can act on.
Once you have fixed the findings, we confirm the fixes hold at no extra cost.
Active Directory penetration testing identifies attack paths involving credentials, excessive privileges, misconfiguration and lateral movement.
An internal penetration test reveals how an attacker could escalate privileges, move between systems and compromise Active Directory after gaining network access.
ISO 27001 does not mandate an annual penetration test, but it is risk-based, and testing is often the clearest way to show that technical vulnerabilities are being found, understood and managed.
We provide independent testing that supports an ISO 27001 programme, scoped to your risks rather than a generic checklist, with a report that feeds straight into your risk register and remediation plan.
Does ISO 27001 require penetration testing?Independent testing provides evidence that these controls work in practice, not just on paper.
It answers a different question from an external test: not can someone get in, but what could they do once they are in. Working from inside your network, as if a laptop had been phished or a rogue device plugged in, we see how far an attacker could move, what they could reach, and whether they could take control.
Lateral movement and privilege escalation, Active Directory weaknesses, credential exposure and harvesting, network segmentation, unpatched internal systems and services, weak internal service configuration, and sensitive data left accessible on file shares. We chain issues together the way a real attacker would to establish genuine impact, not just a list of individual findings.
Yes, and for most organisations it is the heart of an internal test. We look at the misconfigurations and weaknesses that let an attacker escalate from an ordinary account to domain-wide control: weak Kerberos and authentication settings, over-privileged accounts, credential exposure, and the well-known attack paths that lead to a full compromise if they are not closed off.
An experienced, senior tester runs your engagement from scoping to report, with no hand-off to a junior halfway through. Infrastructure testing is delivered to a recognised methodology by a tester holding The Cyber Scheme's Team Leader qualification for infrastructure testing, which is recognised by the NCSC against UK government testing standards, and our lead tester is a UK Cyber Security Council registered Principal (PriCSP) for Security Testing.
We agree the rules of engagement in writing first, avoid genuinely destructive techniques, and can work from a supplied device or a connection into your network. Testing can be scheduled around your quiet periods, and we stay in contact throughout so there are no surprises.
A clear report written for both your board and your technical team: an executive summary, then each finding with a risk rating, the evidence, step-by-step reproduction, and specific remediation advice. Once you have fixed the issues we retest to confirm the fixes hold, at no extra cost.
There is no fixed public price, because it depends on scope: the size of your internal estate, the number of sites and whether Active Directory is involved. Tell us about your environment on a short scoping call and we will come back with a fixed-price quote, typically within 48 hours.
Tell us about your internal network and we'll recommend an appropriate scope and provide a no-obligation quotation.
A real tester, not a sales team, so the first reply is already useful.
15 to 30 minutes to understand your estate and what you need to prove.
Clear scope, clear price, clear dates, typically within 48 hours.
Not sure whether you need internal, external or both? Tell us what you're trying to achieve and we'll help you scope it.