
Why Internal Penetration Testing Matters: The Hidden Risks Inside Your Network
An internal penetration test reveals how an attacker could escalate privileges, move between systems and compromise Active Directory after gaining network access.
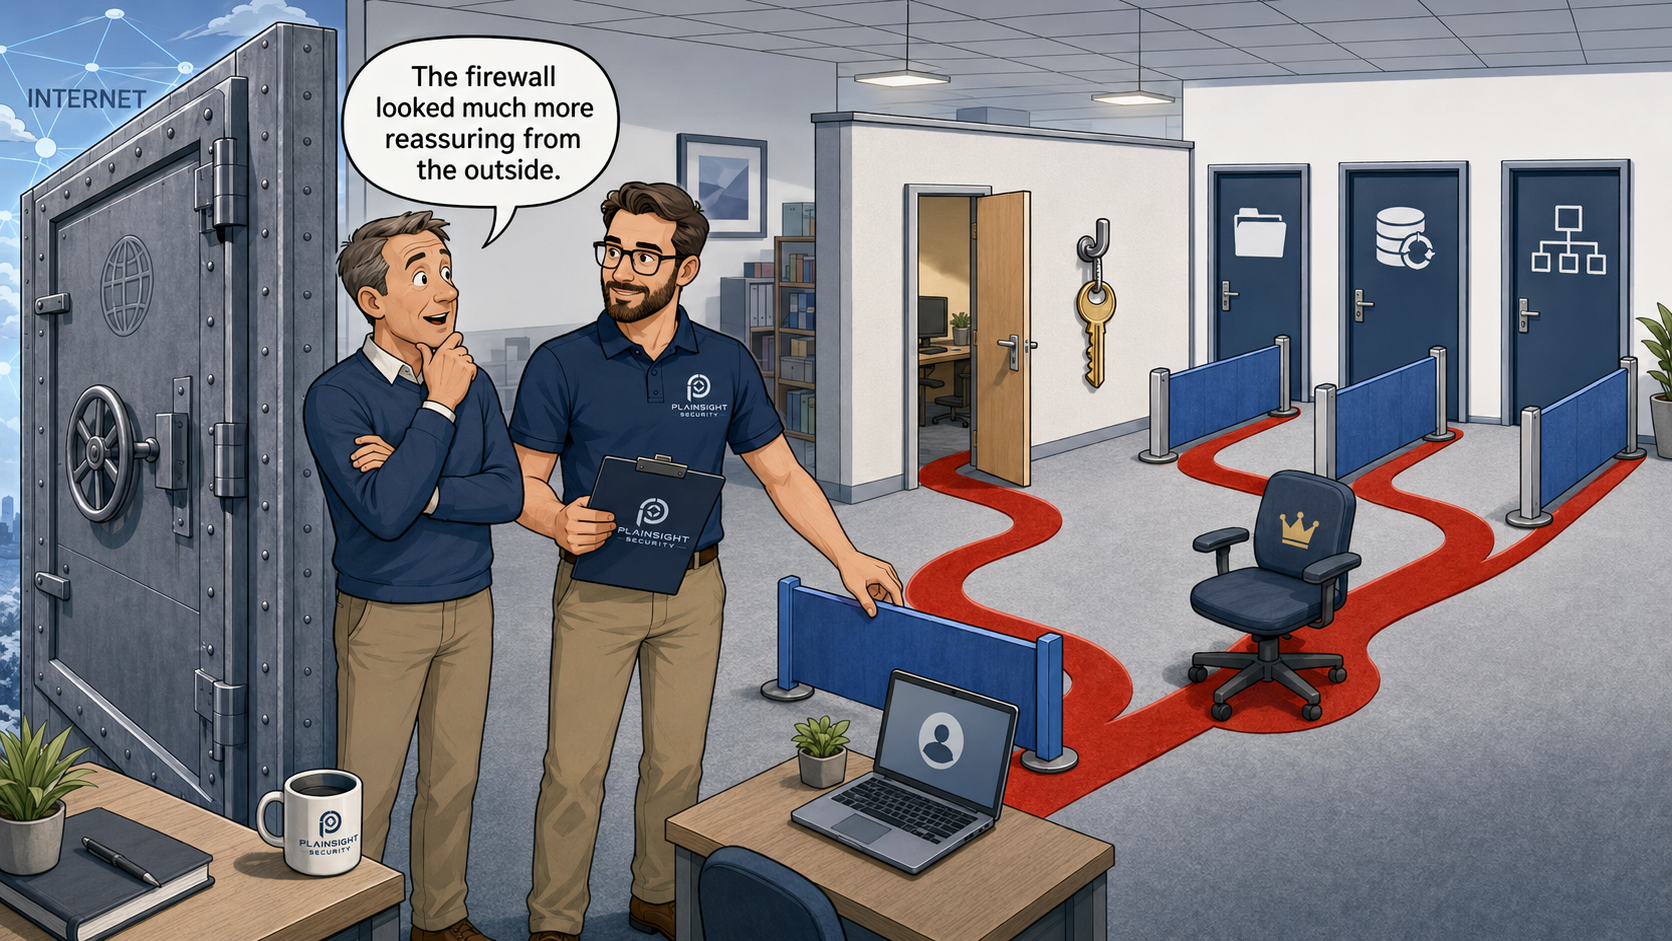
An internal penetration test assesses whether an attacker who has gained access to an organisation's internal network could compromise systems, escalate privileges, access sensitive information or take control of critical infrastructure.
A strong firewall can help keep attackers out. It cannot protect an organisation from an attacker who is already inside.
For organisations with on-premises infrastructure, understanding what happens after an attacker gains an initial foothold can be just as important as understanding how they might get in.
Why test the internal network?
External penetration testing is an important part of understanding your security. It assesses the systems and services that are exposed to the internet and helps determine whether an attacker can gain an initial foothold.
But attackers do not always need to break through the perimeter directly.
An attacker may gain access through:
- Phishing
- Stolen credentials
- Malware
- A compromised laptop
- Remote access services
- A third-party supplier
- A compromised cloud account
- An exposed or vulnerable service
Once an attacker is inside, the question changes.
Instead of:
"Can they get in?"
the question becomes:
"What can they do once they're in?"
This is where internal penetration testing provides valuable insight.
An internal penetration test attempts to simulate the actions of an attacker who already has some level of access to the organisation's internal environment. The objective is to understand whether that initial access can be used to compromise additional systems, obtain higher privileges or ultimately take control of critical infrastructure.
Active Directory: the heart of many Windows networks
For many organisations, Active Directory remains one of the most important components of their internal infrastructure.
Active Directory is used to manage identities, authentication, computers, users and access to resources across a Windows environment. It can control who is allowed to access particular systems and what they are permitted to do.
If an attacker compromises the Active Directory environment, the consequences can extend far beyond a single workstation.
An internal penetration test may therefore examine areas including:
- Domain users and privileged accounts
- Domain administrators
- Privileged groups
- Group Policy
- Service accounts
- Authentication mechanisms
- Domain controllers
- Trust relationships
- Permissions and delegation
- Credential exposure
The important point is not simply whether an individual configuration is technically weak. It is whether weaknesses can be combined to provide an attacker with a path towards increasingly privileged access.
A low-privileged user account may appear relatively harmless in isolation. If that account can be used to obtain credentials, access another server and ultimately compromise a privileged account, the overall risk is considerably more significant.
What happens after an attacker compromises one workstation?
Consider a relatively common scenario.
An employee receives a convincing phishing email and opens a malicious attachment.
The attacker gains control of the employee's workstation.
At this point, they may have limited access and privileges. That does not necessarily mean the attack has failed.
The attacker may attempt to discover credentials, identify other systems, understand the network and find weaknesses that allow them to increase their privileges.
The attack could look something like this:
Initial compromise
An employee opens a malicious attachment.
↓
Internal access
The attacker gains control of their workstation.
↓
Credential discovery
The attacker identifies credentials, sessions or other useful authentication information.
↓
Privilege escalation
A weakness provides a route to higher privileges.
↓
Lateral movement
The attacker gains access to additional systems.
↓
Domain compromise
The attacker eventually obtains highly privileged access to Active Directory.
↓
Business impact
The attacker may be able to access files, systems, accounts and other critical resources.
An internal penetration test attempts to determine whether this type of attack path is actually possible within the organisation's environment.
Importantly, the objective is not to cause damage. Testing is performed within an agreed scope and under controlled conditions to demonstrate what an attacker could potentially achieve.
What does an internal penetration test look for?
The exact scope and methodology will depend on the organisation and the objectives of the engagement.
An internal infrastructure penetration test may examine areas such as:
- Network segmentation
- Unnecessary or exposed services
- Authentication controls
- Password security
- Excessive privileges
- Active Directory configuration
- Privilege escalation
- Lateral movement
- Credential exposure
- SMB security
- Kerberos configuration
- LDAP security
- Group Policy weaknesses
- Service accounts
- Legacy protocols
- Unsupported systems
- Sensitive information exposure
The assessment should not simply produce a list of technical weaknesses.
The real value comes from understanding how those weaknesses can be combined.
For example, a weak permission may appear relatively low risk on its own. But if that permission allows a compromised workstation to obtain credentials for a privileged account, the significance changes considerably.
Why vulnerability scanning isn't enough
Vulnerability scanning and penetration testing serve different purposes.
A vulnerability scanner might identify:
"This server has vulnerability X."
That is useful information, but an internal penetration test asks a different question:
"Can this vulnerability actually be used as part of an attack path to compromise something important?"
Penetration testing can also identify security weaknesses that do not necessarily correspond to a specific CVE.
For example, an attacker might be able to progress through a series of weaknesses:
User → Workstation → Credentials → Server → Privileged Account → Domain Administrator
The individual weaknesses are important, but the attack path provides the business context.
It demonstrates how an attacker could move from an ordinary user-controlled device towards highly privileged access.
This is one of the key differences between identifying vulnerabilities and understanding how an environment could actually be compromised.
Internal penetration testing isn't just for large enterprises
It is easy to assume that internal penetration testing is something only large organisations need to consider.
That is not necessarily the case.
Smaller and mid-sized organisations can have internal environments containing:
- Flat networks
- Limited network segmentation
- Long-lived Active Directory environments
- Excessive administrator privileges
- Legacy systems
- Shared accounts
- Poorly documented permissions
- Unsupported operating systems
- Older applications and protocols
Smaller environments can sometimes provide attackers with fewer obstacles once an initial workstation has been compromised.
For example, if user workstations, file servers, backup systems and domain controllers all sit within a relatively flat network, compromising one endpoint may provide an attacker with considerably more opportunities for lateral movement.
The size of the organisation does not determine whether internal testing is valuable. The complexity and security architecture of the environment do.
What about Microsoft 365?
Moving email and other services to Microsoft 365 does not necessarily mean that an organisation no longer has an internal security boundary.
Many organisations operate a mixture of cloud and on-premises infrastructure.
They may still have:
- On-premises Active Directory
- Hybrid Active Directory
- File servers
- Print servers
- Line-of-business applications
- NAS devices
- Hypervisors
- Backup infrastructure
- Network appliances
- Management systems
In a hybrid environment, the relationship between cloud identities and on-premises infrastructure can also become an important consideration.
Microsoft 365 can remove the need for some traditional infrastructure, but it does not automatically remove the internal attack surface.
If an organisation still operates significant on-premises infrastructure, it is important to understand what an attacker could do after compromising an internal endpoint.
Internal vs external penetration testing
External and internal penetration tests answer different security questions.
| External penetration test | Internal penetration test |
|---|---|
| Simulates an attacker outside the organisation | Simulates an attacker who has gained internal access |
| Tests internet-facing systems | Tests internal systems and networks |
| Examines perimeter security | Examines lateral movement |
| Tests external authentication | Tests internal authentication and privileges |
| Assesses the public attack surface | Assesses the internal attack surface |
| Focuses heavily on initial access | Focuses on privilege escalation and further compromise |
| May identify routes into the organisation | May identify routes towards domain or infrastructure compromise |
Neither approach is inherently a replacement for the other.
For organisations with significant on-premises infrastructure, these tests answer two very different security questions.
An external test can help determine whether an attacker can get in.
An internal test can help determine what happens if they do.
How often should internal infrastructure be tested?
There is no universal rule that means every organisation must perform an internal penetration test at exactly the same interval.
The appropriate frequency depends on the organisation's risk, infrastructure, regulatory requirements and rate of change.
Internal testing can be particularly valuable:
- Periodically as part of a security assurance programme
- After major infrastructure changes
- Following an Active Directory redesign
- Following significant acquisitions or mergers
- After major network segmentation changes
- Following a significant security incident
- When introducing new critical systems
Regular vulnerability scanning can provide ongoing visibility between deeper penetration tests.
This combination can be particularly effective: continuous identification of known vulnerabilities alongside periodic testing of how weaknesses can be combined into realistic attack paths.
What happens after the test?
The value of an internal penetration test should not end when the report is delivered.
A useful assessment should provide the organisation with:
- Clear findings
- Risk prioritisation
- Supporting evidence
- Identified attack paths
- Practical remediation recommendations
- Retesting where appropriate
Attack paths are particularly useful when communicating technical security issues to management.
Compare these two statements:
"Finding 37: Weak permissions."
with:
"This weakness allows a compromised standard user workstation to obtain elevated privileges and potentially compromise the domain."
The second statement provides context.
It explains not just what is wrong, but why it matters.
That makes it easier for an organisation to prioritise remediation and understand which weaknesses should be addressed first.
Your firewall isn't the last line of defence
A firewall is an important security control, but it should not be treated as the final answer to an organisation's security.
If an attacker compromises a workstation, steals valid credentials or gains access through a trusted connection, the internal network becomes the new attack surface.
For organisations running on-premises or hybrid Active Directory, understanding what an attacker can do after gaining an initial foothold is particularly important.
An internal penetration test provides an opportunity to safely simulate that scenario, identify weaknesses in the path from ordinary user to privileged access, and address them before a real attacker gets the opportunity.
The question isn't only whether an attacker can get into your network.
It's what they can do once they're there.
Internal Infrastructure Penetration Testing
Plainsight Security provides internal infrastructure penetration testing designed to identify weaknesses in internal networks, Active Directory environments and systems that could allow an attacker to escalate privileges, move laterally or compromise critical infrastructure.
If your organisation relies on on-premises or hybrid infrastructure, an internal penetration test can help you understand how resilient your environment would be after an attacker gains an initial foothold.

Written by
Mark Tomlinson
Our lead penetration tester, Mark Tomlinson, holds The Cyber Scheme Team Leader qualification in infrastructure penetration testing, an advanced certification recognised by the National Cyber Security Centre (NCSC) and used by professionals testing government systems and UK critical national infrastructure. Mark is also registered with the UK Cyber Security Council as a Principal Cyber Security Professional (PriCSP) specialising in Security Testing and holds an MSc in Computer Science with Cyber Security.
More about how we workPut this into practice.
Cyber Essentials, Cyber Essentials Plus, and penetration testing — fixed-price, plain English, and built to stay out of your way.