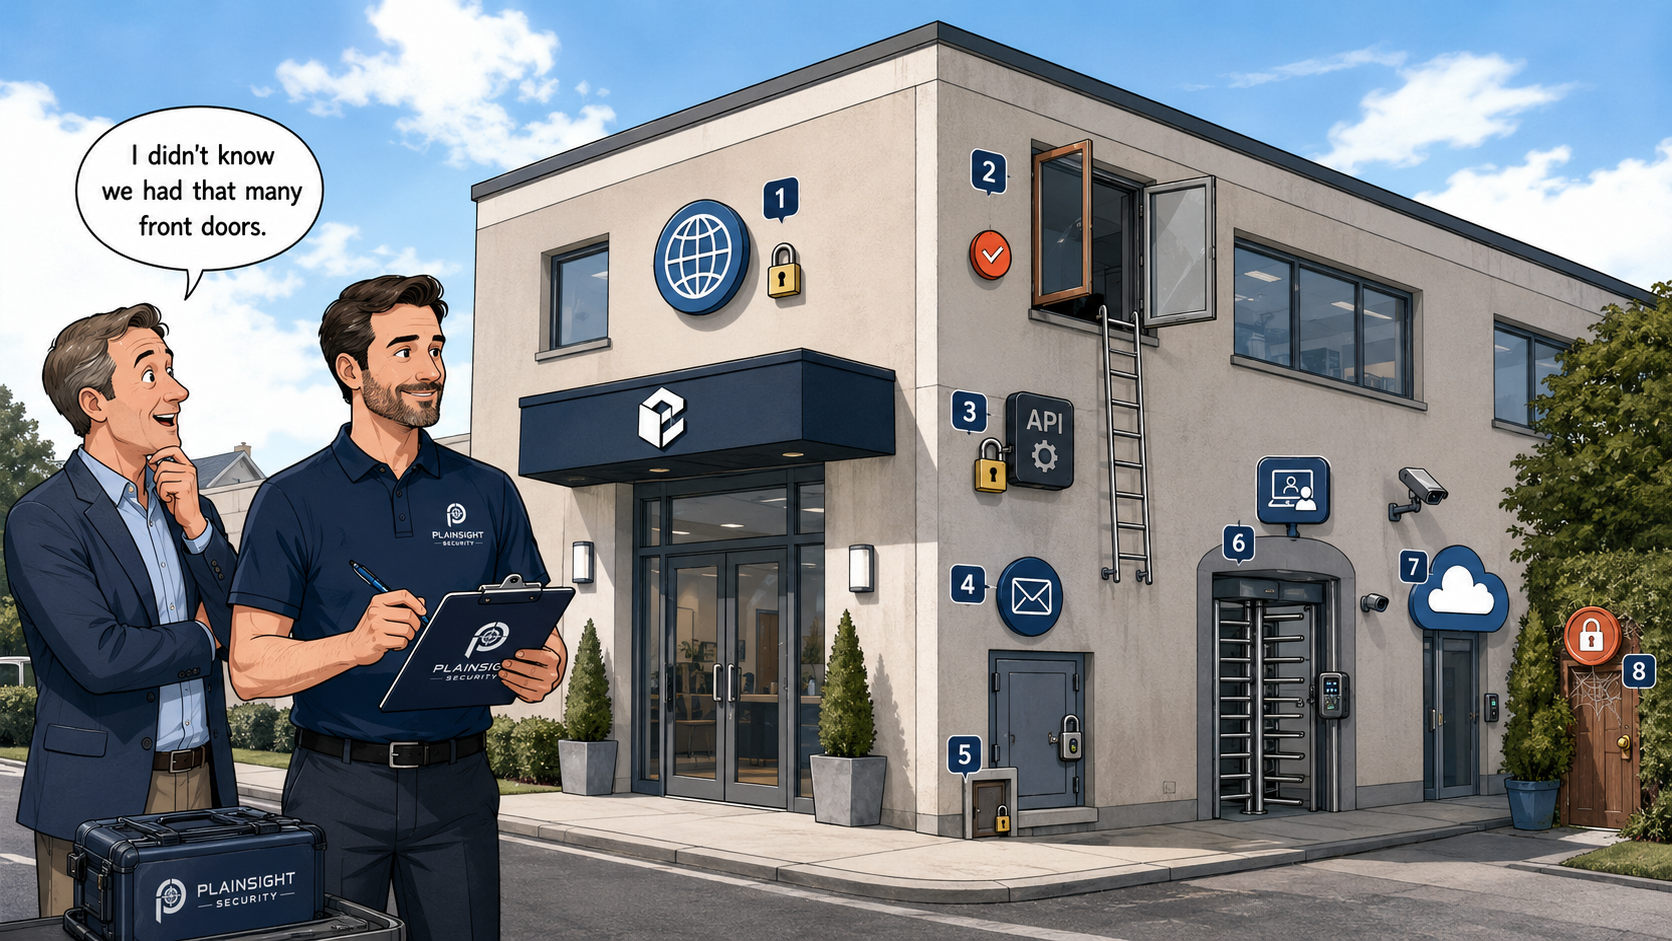
Exposed services and open ports
What is listening on your perimeter, whether it should be, and whether any of it hands an attacker a foothold.

See your internet-facing perimeter the way an attacker does.
Independent, manual testing of everything you expose to the internet, delivered to a recognised methodology by a Cyber Scheme Team Leader qualified tester.
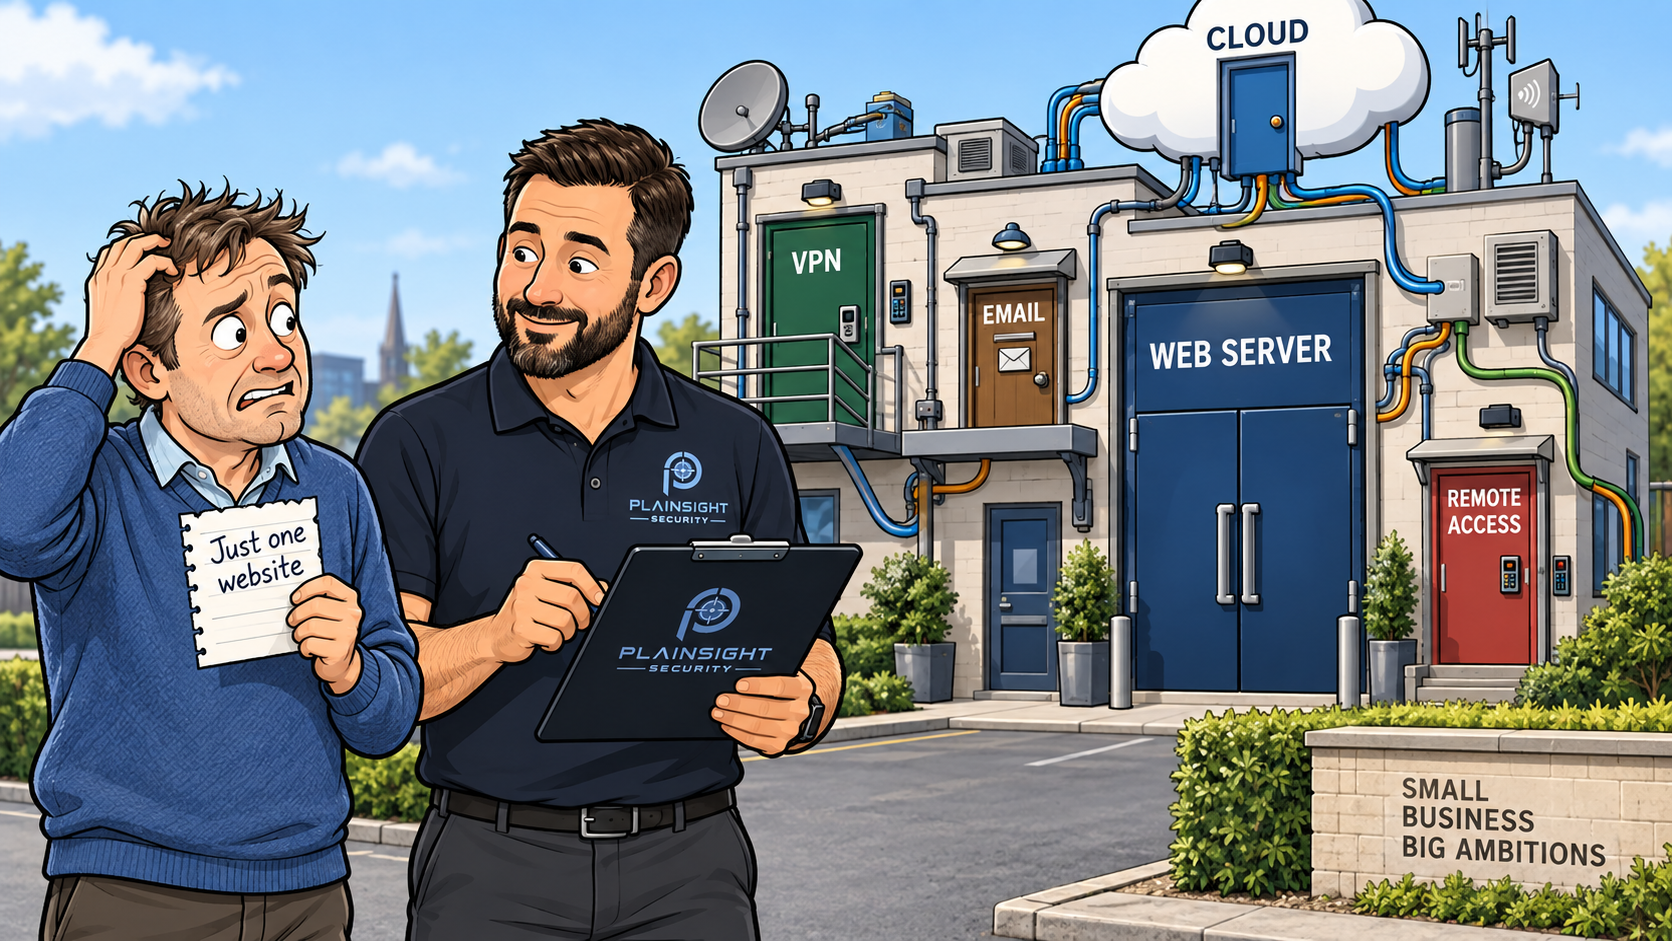
Every service you publish, a website, a mail server, a VPN, a remote-access portal, is reachable by anyone in the world. That reachable surface is where an external attack starts.
We test it with no prior access or credentials, mapping what you expose and then probing it for weaknesses: unpatched services, weak or default credentials, exposed admin interfaces, misconfiguration, and the small information leaks that help an attacker plan. The aim is to establish what someone could actually achieve, and to give you a clear, prioritised list of what to fix first.
What is listening on your perimeter, whether it should be, and whether any of it hands an attacker a foothold.
VPNs, remote desktop and management portals: the doors built for staff that attackers try hardest to walk through.
Internet-facing software running with known, exploitable flaws, validated by hand to rule out false positives.
Default logins, weak passwords and exposed management interfaces that turn a minor exposure into full access.
Firewall and service misconfiguration, weak TLS and certificate handling, and headers that quietly widen your attack surface.
The details you unintentionally publish, in metadata, error messages and exposed files, that help an attacker plan the next step.
Infrastructure testing is delivered to a recognised methodology by a tester holding The Cyber Scheme's Team Leader qualification for infrastructure testing, which is recognised by the NCSC against UK government testing standards. Our lead tester is also a UK Cyber Security Council registered Principal (PriCSP) for Security Testing.
In practice that means industry-standard tooling for breadth, then manual testing to work out what an attacker could really do with what it finds, and a report you can act on rather than a raw export.
A short enquiry, answered by a tester rather than a sales team.
15 to 30 minutes to confirm the hosts, ranges and services in scope.
Clear scope, clear price, clear dates, typically within 48 hours.
Agreed rules of engagement, testing to a recognised methodology, then a report you can act on.
Once you have fixed the findings, we confirm the fixes hold at no extra cost.
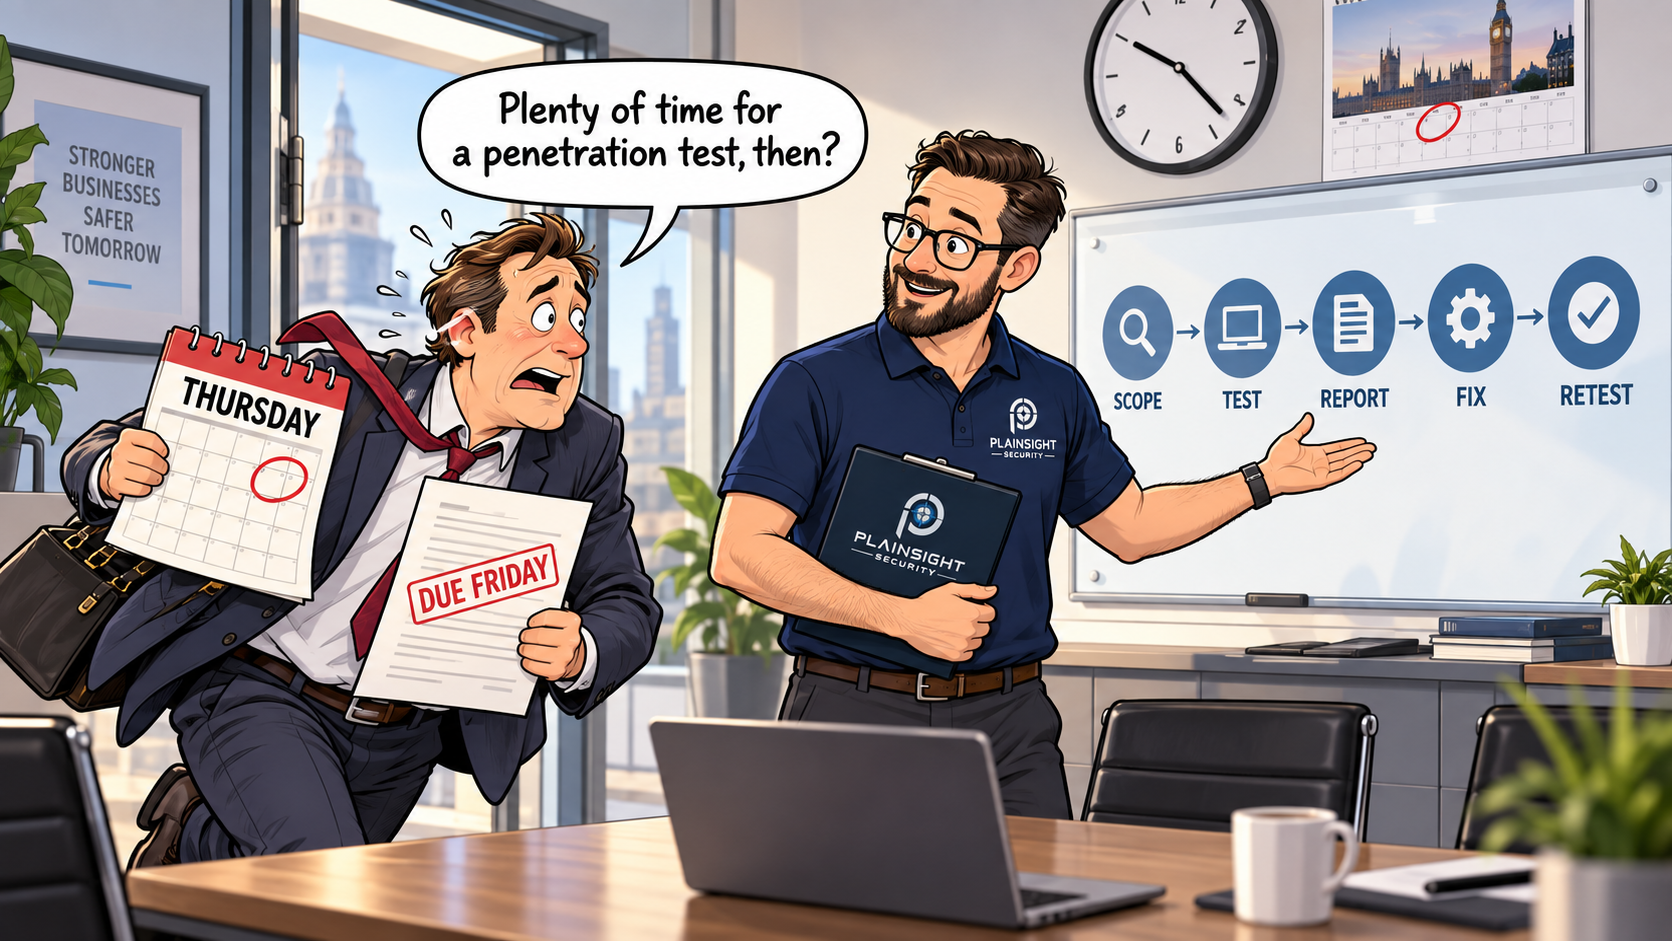
An external penetration test may take one to three testing days or longer. Learn what affects the timescale and how to plan for reporting, remediation and retesting.
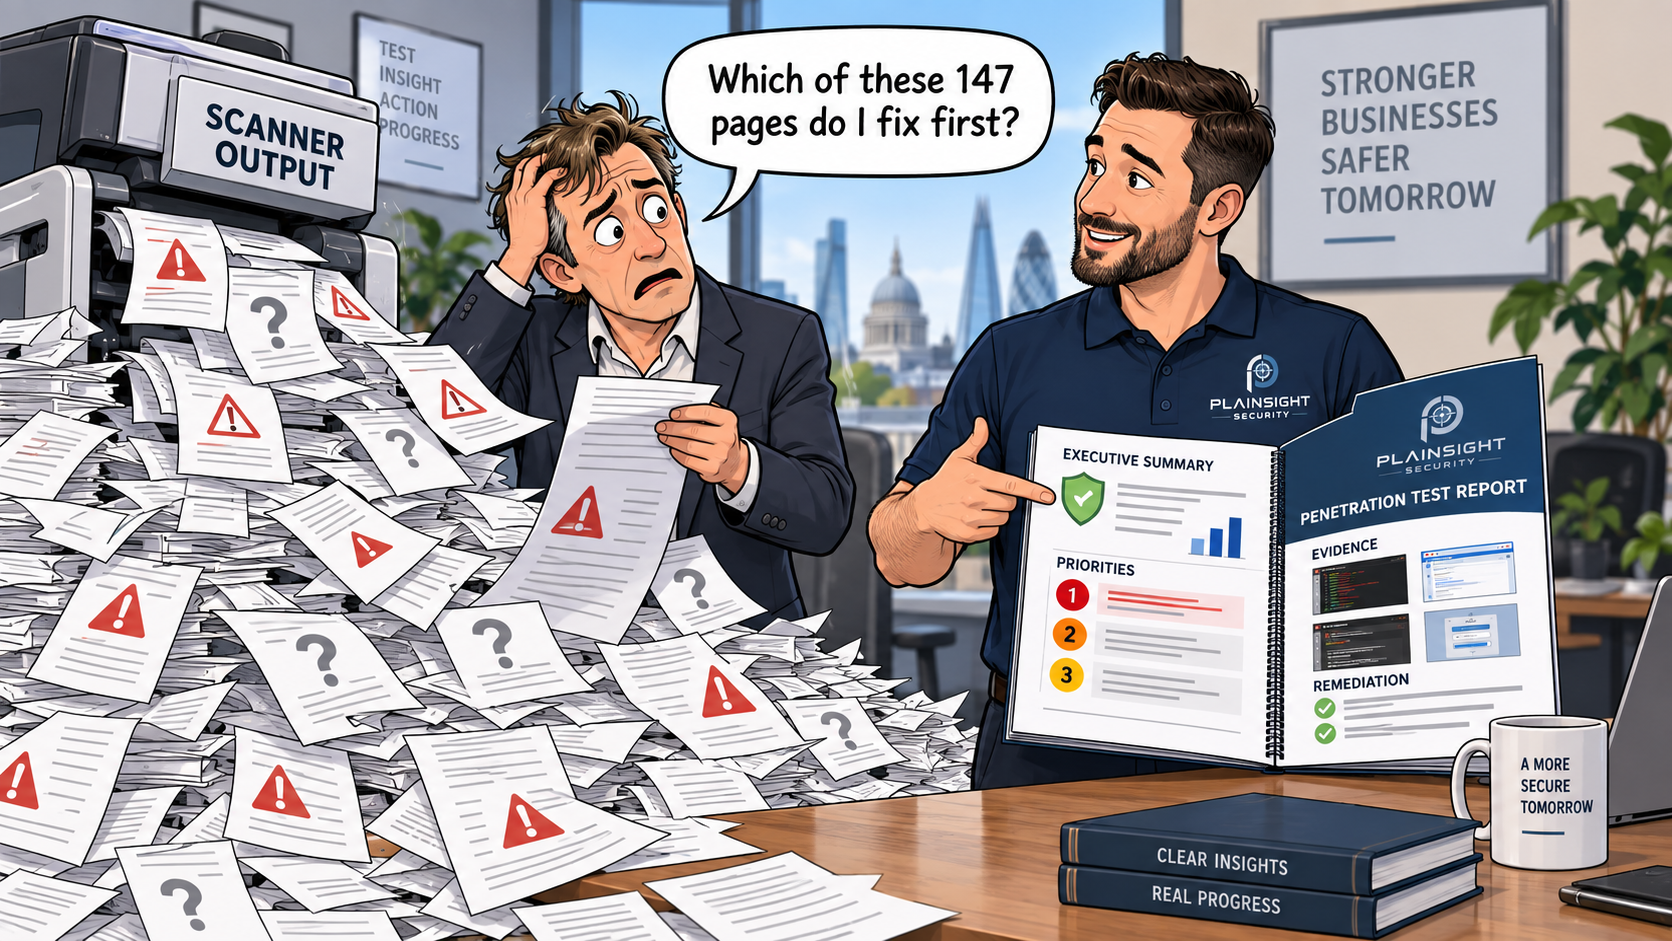
Learn what a professional external penetration test report should include, from validated findings and attack paths to remediation priorities and retesting.
External penetration testing costs depend on the size, complexity and exposure of your internet-facing infrastructure. Learn what affects pricing and how to obtain an accurate quotation.
How often should you conduct an external penetration test? Annual testing is a sensible baseline, with additional tests after significant changes or cyber incidents.
An external penetration test identifies exploitable vulnerabilities in internet-facing systems and provides practical recommendations to reduce risk.
ISO 27001 does not mandate an annual penetration test, but it is risk-based, and testing is often the clearest way to show that technical vulnerabilities are being found, understood and managed.
We provide independent testing that supports an ISO 27001 programme, scoped to your risks rather than a generic checklist, with a report that feeds straight into your risk register and remediation plan.
Does ISO 27001 require penetration testing?Independent testing provides evidence that these controls work in practice, not just on paper.
It is a test of everything your organisation exposes to the internet: the servers, services, remote-access gateways and devices an outsider can reach without any prior access or credentials. We approach it exactly as an external attacker would, mapping your perimeter and then probing it for ways in.
Exposed services and open ports, remote access and VPN gateways, web and mail servers, firewalls and edge devices, along with missing patches and known vulnerabilities, weak or default credentials, exposed management interfaces, certificate and encryption weaknesses, and information leakage that helps an attacker. We then try to establish what could actually be achieved, not just what is theoretically present.
An experienced, senior tester runs your engagement from scoping to report, with no hand-off to a junior halfway through. Infrastructure testing is delivered to a recognised methodology by a tester holding The Cyber Scheme's Team Leader qualification for infrastructure testing, which is recognised by the NCSC against UK government testing standards, and our lead tester is a UK Cyber Security Council registered Principal (PriCSP) for Security Testing.
A scanner is fast and good at breadth, catching known issues and missing patches. It cannot confirm whether a finding is genuinely exploitable, chain several small issues into a real compromise, or rule out false positives. An external penetration test combines that tooling with a skilled tester doing exactly that, so you get a prioritised picture of real risk rather than a raw export.
We agree the rules of engagement in writing before any testing begins, avoid genuinely disruptive techniques against production, and can schedule around your quiet periods. We stay in contact throughout, so there are no surprises and minimal impact on your normal operations.
A clear report written for both your board and your technical team: an executive summary, then each finding with a risk rating, the evidence, step-by-step reproduction, and specific remediation advice. Once you have fixed the issues we retest to confirm the fixes hold, at no extra cost.
There is no fixed public price, because it depends on the size of your perimeter: how many hosts, IP ranges and services are in scope. Tell us what you expose on a short scoping call and we will come back with a fixed-price quote, typically within 48 hours.
Tell us what you expose to the internet and we'll recommend an appropriate scope and provide a no-obligation quotation.
A real tester, not a sales team, so the first reply is already useful.
15 to 30 minutes to understand your perimeter and what you need to prove.
Clear scope, clear price, clear dates, typically within 48 hours.
Not sure whether you need external, internal or both? Tell us what you're trying to achieve and we'll help you scope it.