
What Is an External Penetration Test?
An external penetration test identifies exploitable vulnerabilities in internet-facing systems and provides practical recommendations to reduce risk.
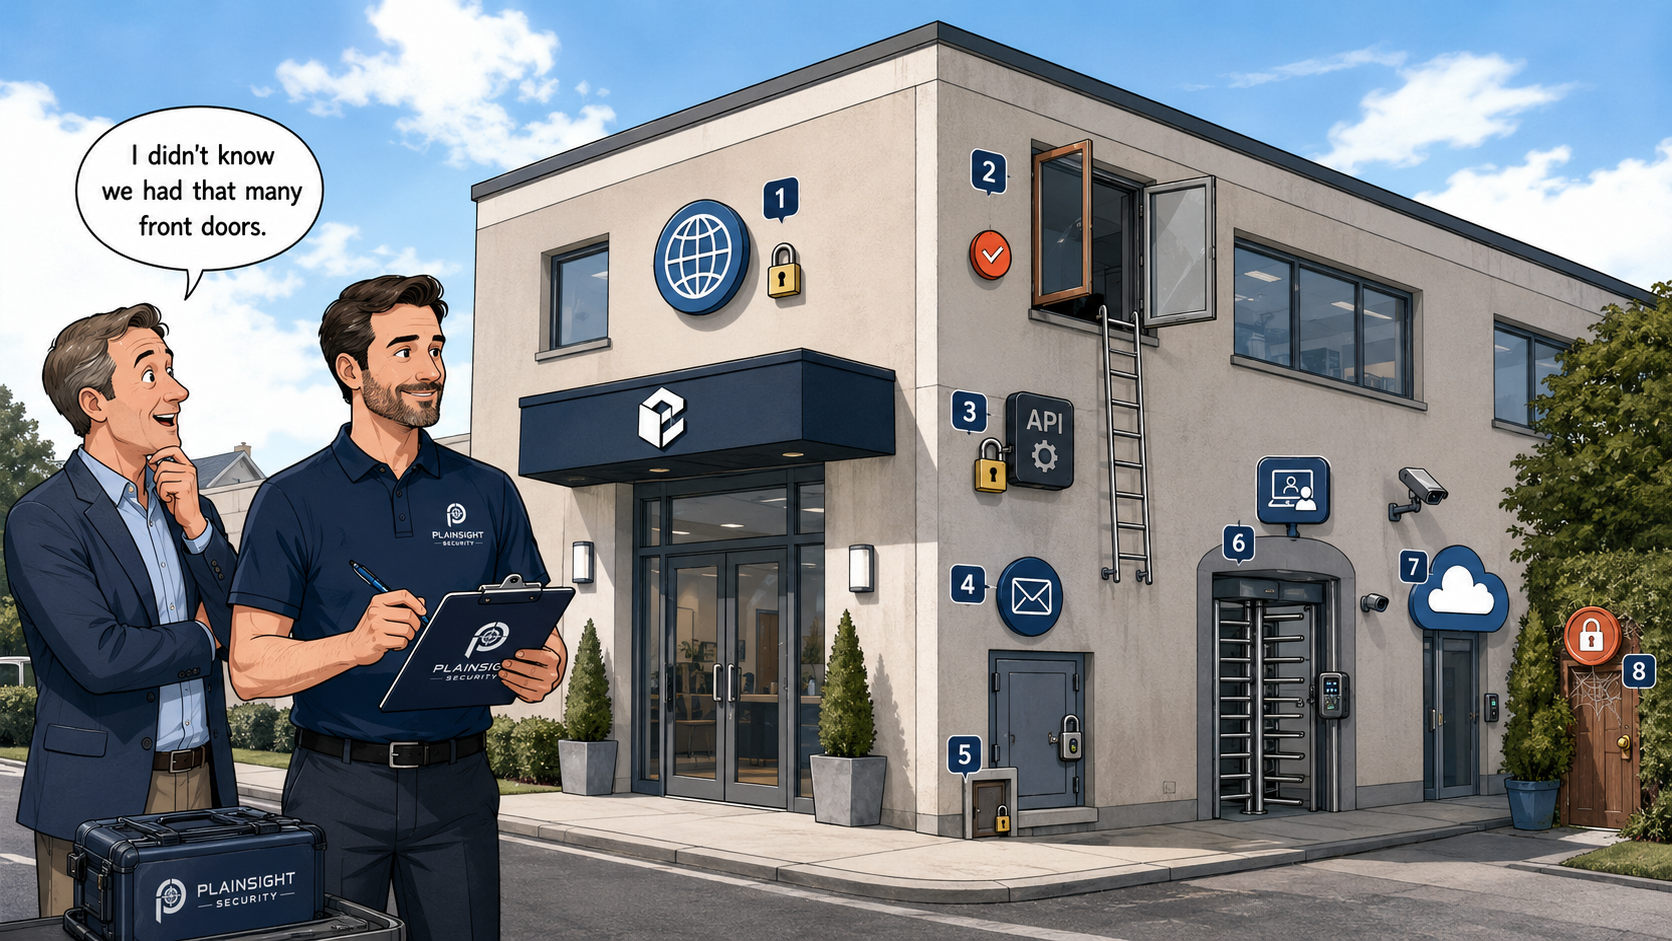
An external penetration test is an authorised security assessment that attempts to identify and exploit vulnerabilities in systems accessible from the internet.
The aim is not simply to find vulnerabilities. A penetration test is designed to establish whether those weaknesses can actually be exploited, what an attacker could achieve, and how serious the resulting risk could be.
For a business, an external penetration test provides a realistic view of how its internet-facing systems might look to an attacker.
What is tested?
An external penetration test focuses on systems that are accessible from outside your organisation.
Depending on the scope, this can include:
- Public-facing websites and web applications
- Internet-facing APIs
- VPN gateways and remote access services
- Firewalls and perimeter security devices
- Mail servers and other externally accessible services
- Cloud-hosted infrastructure
- Remote administration interfaces
- Publicly exposed databases or management services
- Authentication and access-control mechanisms
- TLS/SSL configuration and other security controls
- DNS and externally visible infrastructure
The tester will normally begin by identifying what is exposed to the internet before moving into more detailed testing.
This can reveal systems that an organisation may not realise are publicly accessible.
What isn't tested?
An external penetration test is not automatically an assessment of your entire IT environment.
Unless specifically included within the agreed scope, it will generally not test:
- Internal servers and workstations
- Internal network segmentation
- Employee laptops
- Physical security
- Social engineering or phishing
- Wireless networks
- Source code
- Third-party systems that you do not control
- Systems that are deliberately excluded from the engagement
This distinction is important.
An external penetration test answers the question:
"What could an attacker achieve against our internet-facing systems?"
It does not necessarily answer:
"How secure is our entire organisation?"
The scope should therefore be agreed before testing begins.
How is an external penetration test carried out?
A professional penetration test follows a structured methodology rather than simply running an automated vulnerability scanner.
1. Scoping and authorisation
Before testing starts, the systems, IP addresses, domains and applications included in the assessment are agreed.
Written authorisation is essential. Penetration testing involves deliberately attempting to exploit security weaknesses, so testing systems without permission can have serious legal and operational consequences.
2. Reconnaissance
The tester gathers information about the organisation's external attack surface.
This can include identifying:
- Domains and subdomains
- IP addresses
- Open ports
- Running services
- Technologies and frameworks
- Publicly accessible applications
- Authentication mechanisms
- Cloud infrastructure
- Information accidentally exposed through public sources
The objective is to understand what an attacker can discover before attempting exploitation.
3. Vulnerability identification
The identified services and applications are examined for potential weaknesses.
This may involve both automated tools and manual testing.
Automated tools are useful for identifying large numbers of potential vulnerabilities, but they cannot reliably determine the real-world impact of many application, authentication and access-control weaknesses.
4. Manual exploitation
Potential vulnerabilities are investigated manually to determine whether they are actually exploitable.
Where appropriate, a tester may attempt to demonstrate issues such as:
- Authentication bypass
- Privilege escalation
- Insecure direct object references
- SQL injection
- Cross-site scripting
- Remote code execution
- Information disclosure
- Weak access controls
- Security misconfigurations
Testing is controlled to minimise the risk of disrupting production systems.
5. Reporting
The findings are documented in a report that explains:
- What was discovered
- How the vulnerability works
- The potential impact
- The evidence supporting the finding
- The severity
- Recommended remediation
A good penetration test report should be useful to both technical teams and management.
What are typical findings?
The findings vary considerably between organisations.
Common examples include:
Exposed services
Unnecessary services may be accessible from the internet, increasing the organisation's attack surface.
Weak authentication
Poor password policies, missing multi-factor authentication or weaknesses in authentication mechanisms can allow attackers to gain unauthorised access.
Access-control vulnerabilities
An application may allow one user to access information belonging to another user or perform actions they should not be authorised to perform.
Outdated software
Internet-facing systems may contain vulnerabilities in operating systems, applications, frameworks or third-party components.
Security misconfiguration
Examples include incorrectly configured TLS, unnecessary HTTP methods, exposed administration interfaces or excessive information disclosure.
Injection vulnerabilities
Applications may accept malicious input that is subsequently interpreted as commands or queries.
Information disclosure
Applications and infrastructure can sometimes reveal sensitive technical information through error messages, debugging functionality, configuration files or public DNS records.
Importantly, a penetration test does not simply produce a list of CVEs. The tester considers how vulnerabilities can be combined and what they mean from an attacker's perspective.
How long does an external penetration test take?
There is no universal duration.
The time required depends on the size and complexity of the external attack surface and, particularly, whether web applications are included.
A small organisation with a handful of internet-facing services may require a relatively short assessment.
A larger environment with multiple public IP addresses, applications, APIs, authentication systems and cloud infrastructure may require several days or longer.
As a rough guide, a focused external infrastructure penetration test might take 1 to 3 days, while a larger assessment involving several applications or a substantial attack surface can take considerably longer.
The important consideration is not simply how many days a tester spends testing. The scope and depth of the assessment should be appropriate to the systems and risks being assessed.
Who needs an external penetration test?
External penetration testing can be valuable for any organisation that operates systems accessible from the internet.
It is particularly relevant to organisations with:
- Public-facing websites or applications
- Customer portals
- APIs
- Remote access services
- Cloud infrastructure
- Online payment or booking systems
- Sensitive customer information
- Business-critical internet-facing systems
- Regulatory or contractual security requirements
It can also be useful following significant infrastructure changes, application development or migration to cloud services.
For organisations that have never commissioned a penetration test, an external assessment can provide a useful starting point for understanding their attack surface.
External penetration testing and Cyber Essentials
Cyber Essentials and penetration testing serve different purposes.
Cyber Essentials is a baseline security standard designed to help organisations protect themselves against common cyber attacks.
It covers areas including:
- Firewalls
- Secure configuration
- Security update management
- User access control
- Malware protection
Cyber Essentials is primarily concerned with whether appropriate security controls are implemented.
A penetration test takes a different approach. It attempts to identify and exploit weaknesses in those controls and the systems they protect.
Passing Cyber Essentials therefore does not mean that an organisation has passed a penetration test.
Likewise, commissioning a penetration test does not automatically mean that an organisation meets Cyber Essentials requirements.
They complement one another rather than replace one another.
External penetration testing and Cyber Essentials Plus
Cyber Essentials Plus includes a hands-on technical verification of the organisation's security controls.
The assessment includes testing of the organisation's systems against the Cyber Essentials requirements, including vulnerability scanning and other technical checks.
However, a Cyber Essentials Plus assessment should not automatically be considered equivalent to a full external penetration test.
A penetration test is a broader security assessment intended to investigate and exploit vulnerabilities within an agreed scope.
For organisations that want a deeper understanding of their external attack surface, an external penetration test can therefore provide additional assurance beyond the requirements of Cyber Essentials Plus.
Penetration test vs vulnerability scan
These terms are sometimes used interchangeably, but they describe different activities.
A vulnerability scan uses automated tools to identify potential vulnerabilities.
A penetration test combines automated scanning with manual investigation and exploitation.
For example, a vulnerability scanner might identify an outdated service and report a potential vulnerability.
A penetration tester may investigate whether the vulnerability is actually exploitable, determine what access it provides and establish whether it can be combined with other weaknesses to compromise the system.
In simple terms:
Vulnerability scanning asks: "What might be vulnerable?"
Penetration testing asks: "Can I exploit it, and what can I achieve?"
Both have value. Regular vulnerability scanning is particularly useful for continuous monitoring, while penetration testing provides a deeper point-in-time assessment.
Penetration test vs Cyber Essentials
Cyber Essentials is a security certification scheme.
Penetration testing is a technical security assessment.
Cyber Essentials asks whether an organisation has implemented specified baseline security controls.
A penetration test attempts to find weaknesses that could allow those controls or the systems they protect to be bypassed.
For example, Cyber Essentials may require appropriate access controls to be implemented. A penetration test could then attempt to determine whether an application actually enforces those controls correctly.
They therefore answer different questions:
| Cyber Essentials | Penetration Test | |
|---|---|---|
| Primary purpose | Establish a security baseline | Identify and exploit vulnerabilities |
| Approach | Requirements and verification | Offensive security testing |
| Manual exploitation | None | Core part of the assessment |
| Finds unknown weaknesses | Not its primary purpose | Yes |
| Tests attack paths | No | Yes |
| Produces vulnerabilities | Not primarily | Yes |
| Certification | Yes | No |
For many organisations, the most useful approach is not choosing between them, but using each for what it is designed to do.
What happens after the penetration test?
The report is only the beginning.
Once vulnerabilities have been identified, they should be prioritised and remediated according to their severity and business impact.
The process will typically involve:
- Reviewing the findings with the technical team
- Prioritising vulnerabilities based on risk
- Implementing remediation
- Retesting significant vulnerabilities
- Updating systems and configurations
- Reviewing whether similar weaknesses exist elsewhere
- Establishing processes to prevent the issue recurring
A good penetration test should leave an organisation with a clear understanding of what needs to change, rather than simply a document full of technical findings.
Retesting
Where significant vulnerabilities have been identified and remediated, a retest can verify that the fixes are effective.
This is particularly important for vulnerabilities involving authentication, authorisation or application logic, where simply applying a software update may not be sufficient.
Retesting can provide evidence that the original attack path is no longer viable.
How often should an external penetration test be performed?
There is no single interval that is appropriate for every organisation.
An external penetration test should be considered following significant changes to internet-facing infrastructure or applications, and periodically as part of an organisation's broader security programme.
Organisations with frequently changing infrastructure may also benefit from continuous vulnerability monitoring between penetration tests.
The key is to avoid treating penetration testing as a one-off exercise.
Your external attack surface changes over time. New services are deployed, software is updated, applications change and vulnerabilities are discovered.
A penetration test provides a point-in-time assessment. Combining periodic penetration testing with ongoing vulnerability management provides a much stronger view of your security posture.
Get an independent view of your external attack surface
Your firewall, vulnerability scanner and security controls may all report that your systems are secure.
A penetration test asks a different question:
What can an attacker actually do?
An external penetration test provides an independent assessment of your internet-facing systems, combining automated reconnaissance and vulnerability discovery with manual testing and controlled exploitation.
The result is a practical assessment of your exposure, the vulnerabilities that matter and what you should do about them.
If your organisation relies on internet-facing systems, an external penetration test can provide valuable assurance that your perimeter security is working as intended.

Written by
Mark Tomlinson
Our lead penetration tester, Mark Tomlinson, holds The Cyber Scheme Team Leader qualification in infrastructure penetration testing, an advanced certification recognised by the National Cyber Security Centre (NCSC) and used by professionals testing government systems and UK critical national infrastructure. Mark is also registered with the UK Cyber Security Council as a Principal Cyber Security Professional (PriCSP) specialising in Security Testing and holds an MSc in Computer Science with Cyber Security.
More about how we workPut this into practice.
Cyber Essentials, Cyber Essentials Plus, and penetration testing — fixed-price, plain English, and built to stay out of your way.