
How Long Does an External Penetration Test Take?
An external penetration test may take one to three testing days or longer. Learn what affects the timescale and how to plan for reporting, remediation and retesting.
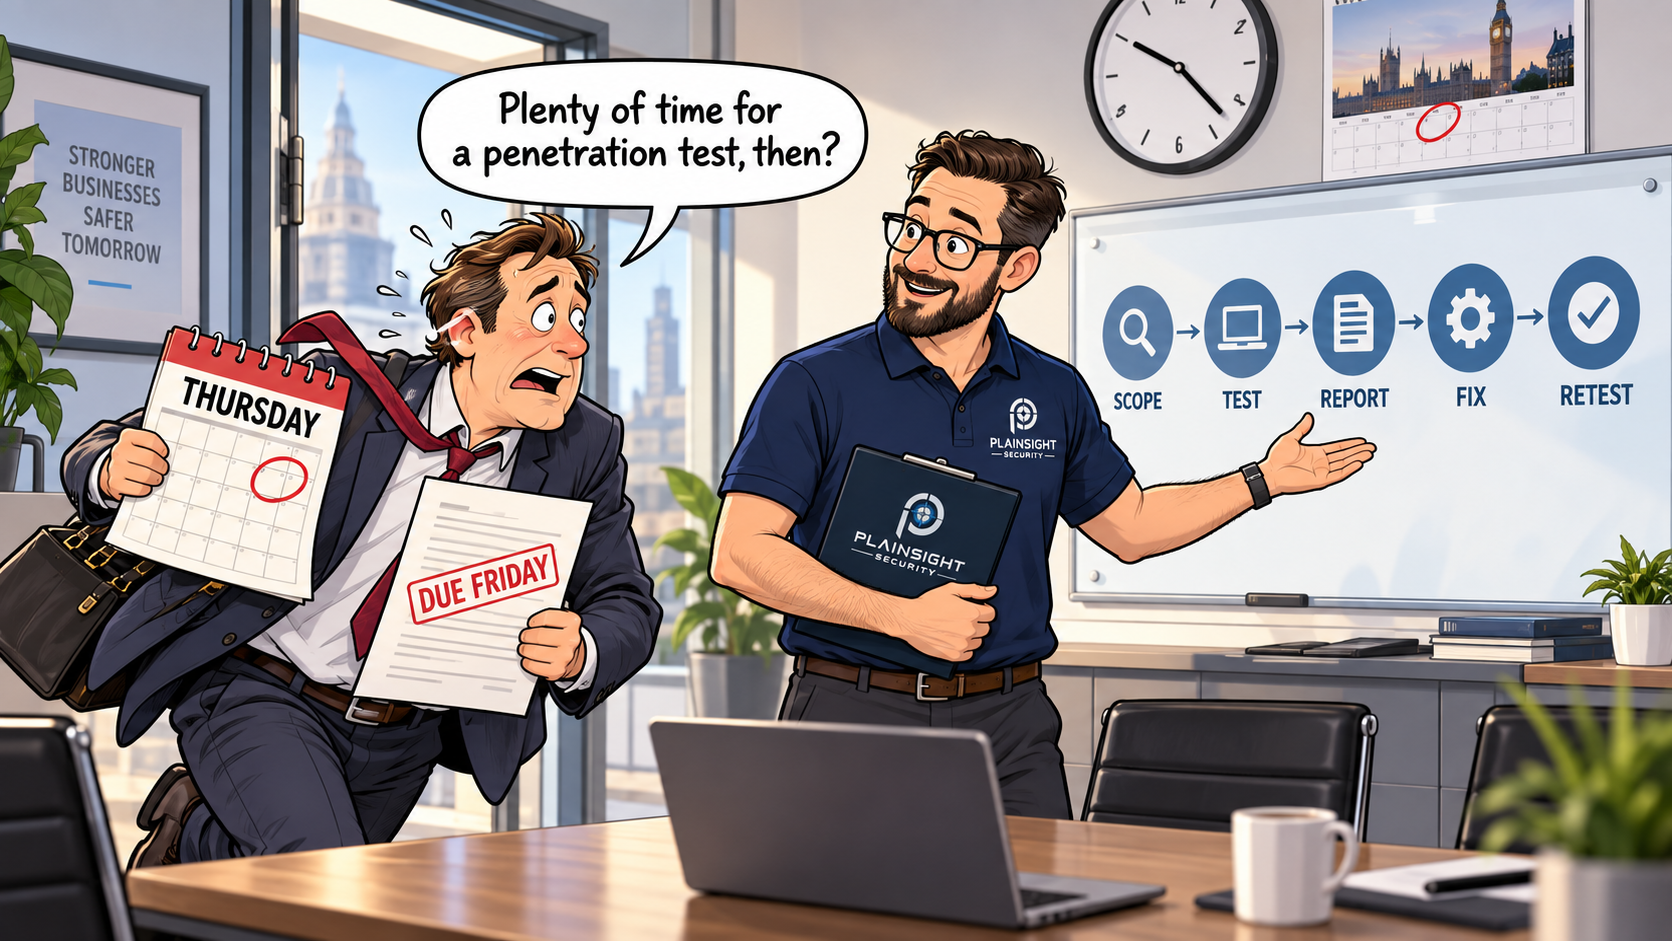
A small, clearly defined external penetration test may require between one and three testing days. An organisation with a larger or more complex internet-facing attack surface may require a week or longer.
However, the testing itself is only one part of the process. Time must also be allowed for scoping, scheduling, reporting, remediation and retesting. If the assessment is needed for a tender, audit, renewal or customer deadline, it is sensible to arrange it as early as possible.
These are representative timescales rather than guarantees. The actual duration depends on the systems exposed to the internet, the depth of testing required and anything encountered during the assessment.
What affects the testing time?
Several factors determine how long an external penetration test will take.
The size of the external attack surface
The external attack surface includes the systems and services that can be reached from the internet. Depending on the organisation, the tester may need to assess:
- Public IP addresses
- VPN gateways
- Firewalls
- Remote-access services
- Email infrastructure
- Cloud-hosted systems
- Internet-facing servers
An organisation with a handful of public addresses and relatively few exposed services may require a short engagement. A business operating multiple locations, network ranges and cloud environments will generally require more testing time.
The number of IP addresses provides a useful starting point, but it should not be the only measure used when estimating the work.
The complexity of the exposed services
A small number of public IP addresses does not necessarily mean that the assessment will be quick.
One address could host several different services, including a VPN, email gateway, remote-access portal and web server. Each service may use different technology and require its own testing approach.
Some systems also warrant more detailed investigation than others. An unusual network service or complex remote-access environment may require additional manual testing, even if the overall number of addresses is relatively small.
The depth of testing
Automated vulnerability scans can often be completed quickly. A professional penetration test takes longer because the tester must interpret and validate the results.
This may involve:
- Manually confirming potential vulnerabilities
- Investigating unusual or unexpected services
- Testing the effectiveness of security controls
- Safely exploring realistic attack paths
- Removing false positives
- Assessing the potential effect on the organisation
This manual analysis is what distinguishes penetration testing from vulnerability scanning. A fast scanner result may identify possible weaknesses, but it may not establish whether they can genuinely be exploited or what they mean for the business.
The stages of an external penetration test
The complete process normally involves five stages.
1. Scoping and quotation
Before testing begins, the provider must establish which systems are included, what must be excluded and what the organisation wants to achieve.
The scoping process should also confirm any deadlines, operational restrictions and third-party systems. A straightforward scope can often be agreed quickly if the organisation already has an accurate list of its public IP addresses and exposed services.
This stage helps ensure the quotation reflects the organisation’s genuine attack surface and that testing is properly authorised.
2. Scheduling and preparation
Once the scope has been agreed, testing dates need to be scheduled and the necessary authorisation documents completed.
The organisation may also need to:
- Notify its IT provider or security monitoring team
- Inform relevant hosting or cloud providers
- Confirm emergency contact details
- Agree permitted testing hours
- Identify any particularly sensitive systems
Some cloud and hosting providers may require advance notification or approval. Leaving this until the planned start date could delay the test.
3. Technical testing
The duration of the testing stage depends on the agreed scope and the complexity of the exposed services.
Testing may also be affected by rate limiting, unstable systems, defensive controls or the need to avoid disrupting a live service. A tester may deliberately reduce the speed of certain activities where aggressive testing could affect availability.
Unexpected findings can also require further investigation. For example, discovering an undocumented remote-access service may create additional work if it falls within the authorised scope.
4. Analysis and reporting
The report will normally follow several working days after the technical testing has finished.
The tester must review the collected evidence, remove false positives, assess the risk of each confirmed finding and develop practical remediation guidance. The report should also include an accessible management summary and explain which issues should be addressed first.
A good penetration test report should not simply be exported from a scanner. Producing a clear, accurate and useful report requires careful analysis after the active testing has been completed.
5. Remediation and retesting
Once the report has been delivered, the organisation must correct the identified weaknesses. The tester can then verify whether each issue has been resolved.
This stage frequently takes longer than the original test. The timescale will depend on the nature of the findings and the availability of internal teams, IT providers, software suppliers or hosting companies.
Some issues may be fixed through a simple configuration change. Others may require an upgrade, replacement system or wider infrastructure change.
Planning around a deadline
If the penetration test is required for a tender, audit, renewal or customer request, work backwards from the final completion date.
Allow time for:
- Scoping and scheduling
- The initial technical test
- Report preparation
- Remediation
- Retesting
- Unexpected delays
Booking the test immediately before a deadline creates a significant risk. Even if the initial testing and report are completed in time, there may be no opportunity to fix and retest any weaknesses that are discovered.
Beginning the process early provides greater flexibility and reduces the pressure on everyone involved.
How can the process be made quicker?
Good preparation can help prevent unnecessary delays. Before contacting a testing provider, try to assemble:
- An accurate list of public IP addresses
- Details of internet-facing services
- A list of clear exclusions
- Any required supplier or hosting approvals
- Emergency contact information
- Internal availability for technical questions
- Sufficient time for remediation
Do not worry if your organisation does not have all this information immediately. A penetration testing provider can help identify the appropriate scope.
Establishing a realistic testing schedule
The time required for an external penetration test should reflect the organisation’s genuine internet exposure rather than an arbitrary number of IP addresses.
A small assessment may require one to three testing days, while larger environments may take a week or more. The complete engagement will take longer once scoping, reporting, remediation and retesting are included.
If you have an upcoming tender, audit, renewal or customer deadline, Plainsight Security can help scope the work and establish a realistic testing and reporting schedule. Contact us as early as possible to discuss your external infrastructure.

Written by
Mark Tomlinson
Our lead penetration tester, Mark Tomlinson, holds The Cyber Scheme Team Leader qualification in infrastructure penetration testing, an advanced certification recognised by the National Cyber Security Centre (NCSC) and used by professionals testing government systems and UK critical national infrastructure. Mark is also registered with the UK Cyber Security Council as a Principal Cyber Security Professional (PriCSP) specialising in Security Testing and holds an MSc in Computer Science with Cyber Security.
More about how we workPut this into practice.
Cyber Essentials, Cyber Essentials Plus, and penetration testing — fixed-price, plain English, and built to stay out of your way.