
How Much Does an External Penetration Test Cost?
External penetration testing costs depend on the size, complexity and exposure of your internet-facing infrastructure. Learn what affects pricing and how to obtain an accurate quotation.
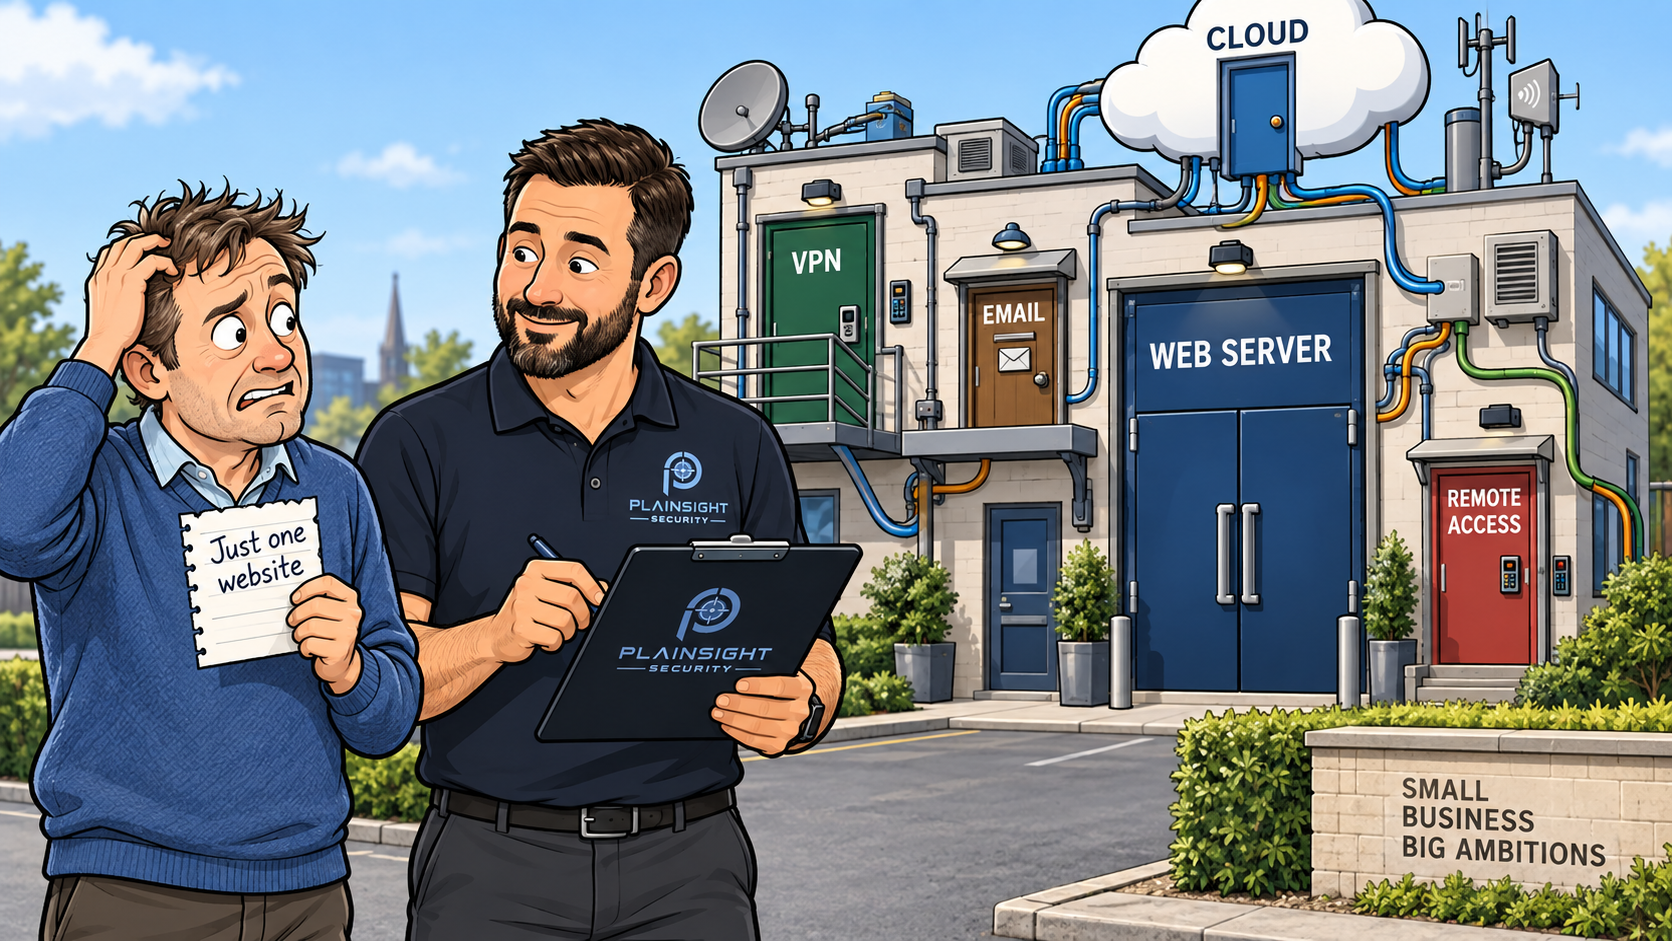
The cost of an external penetration test depends mainly on the size and complexity of your organisation’s internet-facing infrastructure. Tests are normally priced according to the number of testing days required, with smaller and clearly defined environments generally costing less than complex infrastructures spread across multiple locations or cloud platforms.
There is no single price that will suit every organisation. A business with a handful of public IP addresses and limited exposed services may only require a short engagement. An organisation operating numerous servers, VPN gateways, remote-access systems and cloud environments will usually require more time.
For this reason, a properly scoped quotation is far more useful than a generic headline price. It ensures that the systems presenting a genuine risk are included, without asking you to pay for unnecessary testing.
What affects the cost of an external penetration test?
Several factors determine how much testing time will be needed.
Number of public IP addresses
The number of public IP addresses provides a useful starting point, but it does not tell the whole story.
An organisation might own a large range of addresses, many of which have no services exposed to the internet. Conversely, a single public IP address could host several different services, each requiring careful assessment.
A penetration testing provider should therefore consider what is actually accessible on each address, rather than simply multiplying the number of addresses by a fixed price.
Number and type of exposed services
The services available from the internet have a significant effect on the time required. These might include:
- VPN gateways
- Firewalls
- Remote-access portals
- Email services
- Web servers
- File-transfer services
- Cloud-hosted infrastructure
- Remote administration interfaces
Different services require different testing techniques. A VPN gateway, for example, may need to be assessed for configuration weaknesses, information disclosure and authentication issues. An email server may require tests for insecure protocols, user enumeration or weaknesses that could support password attacks.
The more technologies involved, the more time the tester may need to investigate them properly.
Complexity of the infrastructure
External infrastructure is not always contained within one neat network range.
An organisation may operate from several locations, use multiple hosting providers or maintain services across platforms such as Microsoft Azure and Amazon Web Services. It may also rely on third-party suppliers for particular systems.
This does not automatically make the test expensive, but it can increase the effort required to identify assets, confirm ownership, define exclusions and test the environment safely.
A clear scope helps prevent important systems from being missed while avoiding unauthorised testing of infrastructure belonging to someone else.
The depth of testing
A manual penetration test costs more than a basic vulnerability scan because it involves considerably more work.
Automated scanning tools can identify missing security updates, exposed services and some common configuration problems. However, their findings may contain false positives or lack the context needed to explain the real risk.
During a penetration test, the tester manually validates findings, investigates unusual behaviour and considers whether several weaknesses could be combined into a realistic attack path. Where appropriate and safe, the tester may attempt controlled exploitation to demonstrate the potential impact.
This additional work is what distinguishes a penetration test from a vulnerability scan.
Reporting and retesting
The quotation should clearly explain what happens after the technical testing has been completed.
A professional external penetration test will normally include:
- A management summary written for non-technical readers
- Detailed technical findings and supporting evidence
- Clear risk ratings
- Practical remediation advice
- A meeting to discuss the results
- Retesting after agreed fixes have been applied
Retesting is particularly important because it provides confirmation that the reported weaknesses have been addressed successfully. Some providers include one round of retesting within the original price, while others charge separately, so this should be confirmed before commissioning the work.
Why the cheapest quotation may not offer the best value
A particularly low quotation is not necessarily a bargain. It may represent little more than an automated vulnerability scan with a generated report.
Before comparing prices, check whether each provider is offering the same level of service. Does the work include genuine manual testing? Will findings be verified? Will the tester investigate whether weaknesses can be exploited or combined? Are detailed remediation guidance and retesting included?
An inexpensive scan may produce a long list of technical observations without explaining which issues genuinely place the organisation at risk. A properly conducted penetration test should provide clear, prioritised findings that help you decide what needs to be fixed first.
The qualifications and experience of the person performing the test should also form part of your decision. The quality of the result depends heavily on the tester’s technical ability, judgement and understanding of real-world attack methods.
How to obtain an accurate quotation
Obtaining a quotation should not require a lengthy technical exercise. A testing provider will normally ask for:
- Public IP addresses or network ranges
- A list of known internet-facing services
- Details of relevant cloud-hosted systems
- Any systems that must be excluded
- Preferred testing dates
- The reason for the test, such as a tender, audit, insurance or customer requirement
Do not worry if you do not have all this information immediately. A good provider can help you identify the appropriate scope and explain what should be included.
It is also worth mentioning any deadlines at the beginning. If the test is required to support a contract, audit or customer request, the provider can ensure that sufficient time is allowed for testing, reporting, remediation and retesting.
A proportionate approach to external penetration testing
External penetration testing should be proportionate to your organisation’s exposure and business needs. A small business should not have to pay for an engagement designed for a large enterprise, while a complex environment should not be squeezed into an unrealistically short assessment.
Plainsight Security provides independently scoped external penetration testing for organisations of all sizes. Contact us with a few details about your internet-facing infrastructure, and we will provide a clear quotation based on the systems that genuinely need to be tested.

Written by
Mark Tomlinson
Our lead penetration tester, Mark Tomlinson, holds The Cyber Scheme Team Leader qualification in infrastructure penetration testing, an advanced certification recognised by the National Cyber Security Centre (NCSC) and used by professionals testing government systems and UK critical national infrastructure. Mark is also registered with the UK Cyber Security Council as a Principal Cyber Security Professional (PriCSP) specialising in Security Testing and holds an MSc in Computer Science with Cyber Security.
More about how we workPut this into practice.
Cyber Essentials, Cyber Essentials Plus, and penetration testing — fixed-price, plain English, and built to stay out of your way.