
Cyber Essentials Plus for MSPs and Their Customers: A Practical Guide
A practical guide to Cyber Essentials Plus for MSPs, covering customer preparation, assessment, remediation and ongoing compliance.
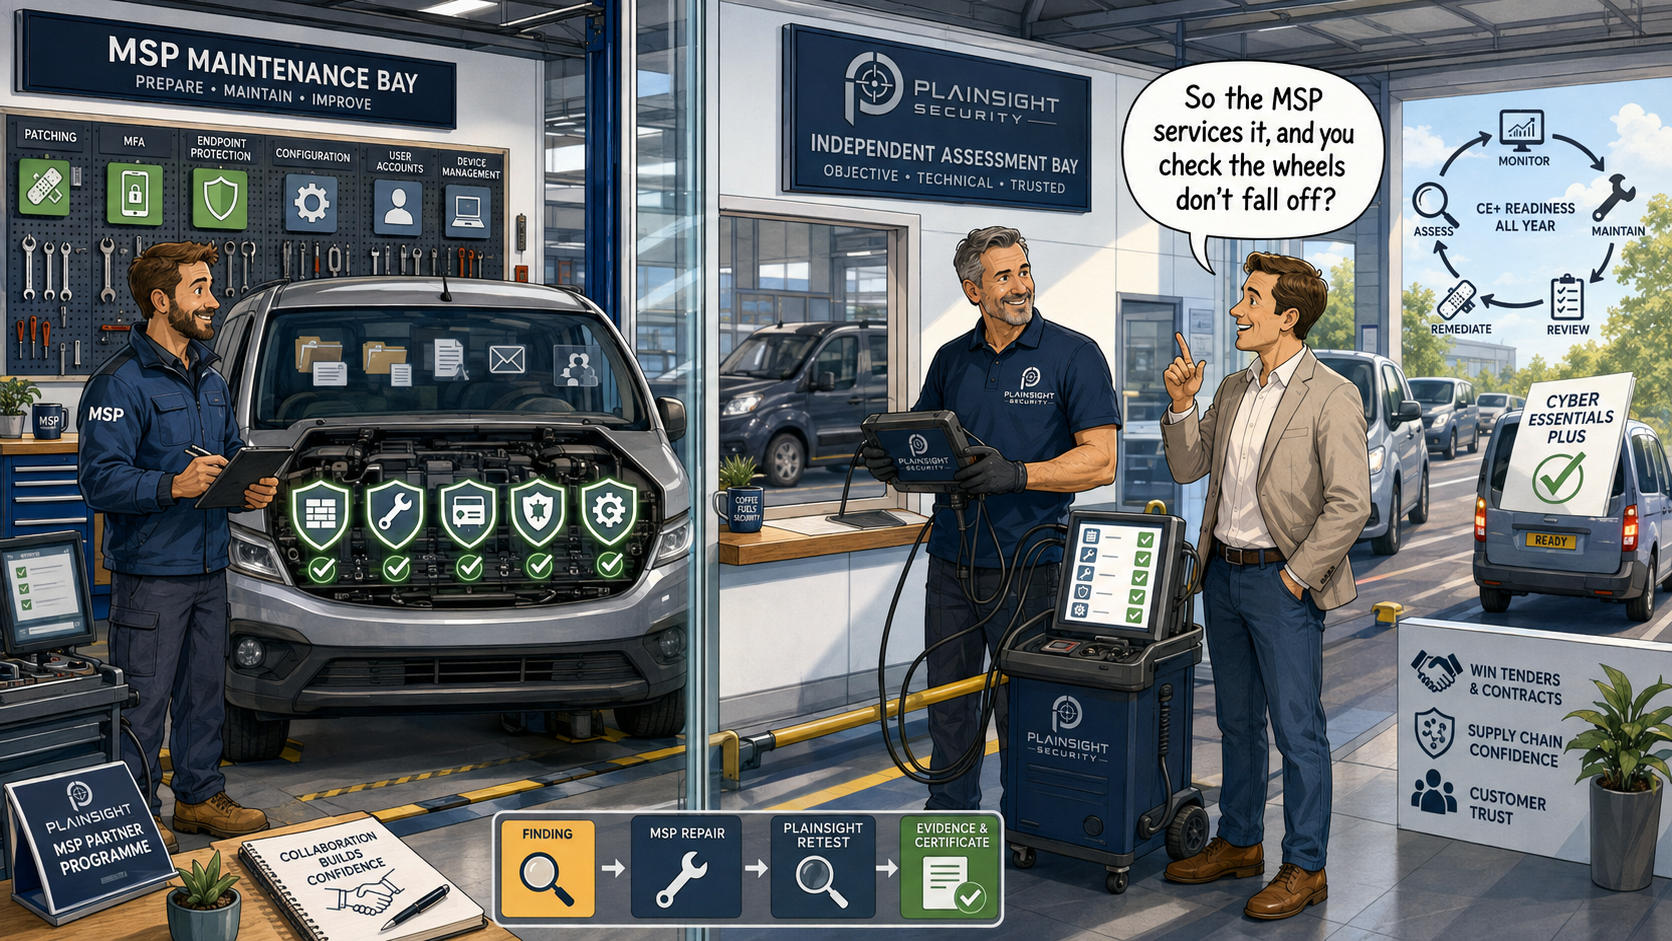
Cyber Essentials Plus (CE+) is the independently verified version of Cyber Essentials, combining the Cyber Essentials self-assessment with hands-on technical testing. For managed service providers (MSPs), it provides an opportunity to help customers demonstrate that their security controls work in practice, while giving the MSP a structured framework for improving and maintaining their customers' security posture.
For an MSP, CE+ does not have to be another administrative burden. Done properly, it can become part of a wider security process that benefits both the MSP and its customers.
What is Cyber Essentials Plus?
Cyber Essentials is a UK government-backed scheme designed to help organisations protect themselves against common cyber threats. It provides a baseline set of technical controls covering areas such as secure configuration, access control, malware protection, security updates and firewalls.
Cyber Essentials is based primarily on a self-assessment. The organisation answers questions about its environment and the security controls it has in place.
Cyber Essentials Plus goes a step further.
With CE+, the organisation's Cyber Essentials requirements are independently assessed through technical testing. This provides additional assurance that the security controls described in the assessment are actually implemented and working as expected.
The technical assessment broadly examines areas such as:
- Internet-facing systems
- Internal devices
- User accounts and access controls
- Security configuration
- Security updates and patching
- Malware protection
- Firewall configuration
- Device security
The result is a significantly stronger level of assurance than relying solely on an organisation's own assessment of its security controls.
For a more detailed explanation, see our guide to [What is Cyber Essentials Plus?].
Why Should MSPs Care About CE+?
MSPs are often responsible for implementing and maintaining many of the technical controls that underpin a customer's Cyber Essentials and CE+ certification.
Consider the systems and services an MSP may manage every day:
- Endpoint configuration
- Patch management
- User accounts
- Administrator privileges
- Multi-factor authentication
- Firewalls
- Secure configuration
- Vulnerability management
- Device management
- Microsoft 365
- Remote access
- Endpoint security
These are not separate from cybersecurity. They are fundamental parts of maintaining a secure IT environment.
CE+ therefore provides an opportunity for an MSP to demonstrate that the security work it performs for customers is having the intended effect.
Rather than simply telling a customer that their systems are secure, an MSP can help them prepare for an independent assessment that tests those controls.
This can be particularly valuable where the customer needs to demonstrate its security posture to clients, suppliers, insurers or other stakeholders.
How CE+ Can Benefit MSP Customers
From the customer's perspective, CE+ provides more than a certificate.
Demonstrating Security
CE+ provides independent evidence that an organisation has met the requirements of the scheme and that its security controls have been technically assessed.
This can be much more meaningful to customers and stakeholders than simply stating that appropriate security measures are in place.
Meeting Customer Requirements
Larger organisations increasingly want evidence that their suppliers have appropriate cybersecurity controls.
Cyber Essentials or Cyber Essentials Plus may form part of supplier security requirements, procurement processes or contractual arrangements.
Having CE+ certification can therefore help an organisation demonstrate that cybersecurity is being taken seriously.
Supporting Supply Chain Assurance
Organisations rarely operate in isolation.
A security weakness in one supplier can potentially create risk for another organisation further up the supply chain.
CE+ can provide useful evidence that an organisation has implemented a defined baseline of security controls and has had those controls independently tested.
Identifying Weaknesses
One of the most useful aspects of an independent assessment is that it can uncover issues that the organisation and its MSP may not have identified.
A configuration may have changed. A device may have been missed. A system may no longer be supported. An account may have excessive privileges.
These issues are much easier to address when they are identified before they contribute to a security incident.
Building Customer Confidence
There is a significant difference between saying:
"Our IT is secure because our MSP looks after it."
and being able to say:
"Our security controls have been independently assessed."
CE+ helps provide that additional level of confidence.
The MSP's Role in Preparing for CE+
An MSP can play an important role in helping a customer prepare for CE+.
Before an assessment, the MSP can review areas such as:
- Hardware and software inventories
- Supported operating systems
- Security update and patch levels
- User accounts
- Administrator privileges
- Multi-factor authentication
- Firewall configuration
- Endpoint security
- Secure configuration
- Device management
- Remote access
- Vulnerability management
The objective should not simply be to make the customer "pass the test".
The objective should be to ensure that the customer's environment is genuinely secure and that the controls required by Cyber Essentials are properly implemented.
This distinction matters.
Preparing a customer for CE+ is different from independently conducting the CE+ assessment.
An MSP can provide remediation, configuration and security advice while an independent certification body performs the assessment.
That separation helps preserve the independence and credibility of the certification process.
Why MSPs Shouldn't Mark Their Own Homework
An MSP may know a customer's infrastructure better than anyone else.
That is extremely valuable when it comes to managing and securing the environment.
However, it can also create a conflict of interest if the same organisation is responsible for implementing the controls and independently deciding whether those controls meet the requirements of a certification assessment.
Independent assessment provides a different perspective.
The benefits include:
- Independent verification
- Objective findings
- A fresh perspective on the environment
- Reduced conflicts of interest
- Greater confidence in the assessment results
The purpose of CE+ is not simply to confirm what an MSP already believes about its customer's environment. The independent assessment provides additional assurance that the required controls are actually present and functioning as expected.
For MSPs, this should not be viewed as a threat to the relationship with the customer.
It can actually strengthen it.
The MSP remains responsible for managing and improving the customer's technology environment, while the independent security provider provides an objective assessment of that environment.
What Happens If a Customer Doesn't Pass?
This is often one of the biggest concerns for organisations considering CE+.
A failed assessment does not mean that the exercise was a failure.
In many cases, identifying a problem before it becomes a security incident is exactly why independent testing is valuable.
The process can be thought of as:
Identify the issue
The assessment identifies where the organisation does not meet the relevant requirements.
↓
Understand the cause
The MSP and customer determine why the issue exists.
It might be caused by outdated software, incorrect configuration, an unsupported operating system, excessive privileges or another technical issue.
↓
Remediate
The MSP addresses the underlying problem.
↓
Retest
Where appropriate, the relevant controls can be reassessed.
↓
Certification
Once the requirements have been satisfied, the customer can proceed with certification.
The important point is that an assessment should be viewed as part of improving security, rather than simply as a pass-or-fail exam.
Finding a weakness before an attacker finds it is a positive outcome.
CE+ Shouldn't Be Treated as a Once-a-Year Project
One of the biggest mistakes an organisation can make is treating CE+ as something that only matters immediately before the annual assessment.
IT environments change constantly.
New laptops are deployed. Users join and leave. Software is installed. Systems are replaced. Configuration changes are made. Vulnerabilities are discovered.
A customer can therefore be fully compliant when an assessment takes place and have a significantly different environment several months later.
MSPs are ideally positioned to help prevent this.
Instead of treating CE+ as an annual scramble, organisations can build readiness into their normal managed service processes:
Monitor → Maintain → Review → Remediate → Assess → Repeat
This might include:
- Regular patch management
- Vulnerability scanning
- Configuration reviews
- User and access reviews
- Device monitoring
- Security reporting
- Regular review of unsupported software
- Ongoing remediation of security issues
The annual CE+ assessment can then become the independent verification of an existing security process, rather than a last-minute attempt to fix months of accumulated problems.
CE+ and Vulnerability Management
Vulnerability management can be particularly useful for maintaining CE+ readiness between assessments.
A CE+ assessment provides an assessment of the environment at a particular point in time.
Vulnerability management provides ongoing visibility as that environment changes.
For example, an organisation might have a fully patched environment when its CE+ assessment takes place. A new vulnerability could subsequently be disclosed in software running on its endpoints or servers.
The organisation's security position has now changed.
Regular vulnerability management can help identify these changes and give the MSP an opportunity to remediate them before they become a larger problem.
In simple terms:
CE+ provides independent verification. Vulnerability management helps maintain visibility between assessments.
The two can therefore work particularly well together.
CE+ and Penetration Testing Are Not the Same Thing
Cyber Essentials Plus and penetration testing are sometimes confused, but they have different purposes.
| Cyber Essentials Plus | Penetration Testing |
|---|---|
| Verifies defined security controls | Attempts to identify and exploit weaknesses |
| Structured certification assessment | Security assessment |
| Focuses on Cyber Essentials requirements | Can investigate broader attack scenarios |
| Designed around baseline security | Can explore complex attack paths |
| Provides independent technical verification | Provides an attacker-focused assessment |
A penetration test may identify vulnerabilities or attack paths that fall outside the scope of Cyber Essentials Plus.
Likewise, an organisation can have a successful penetration test while still having weaknesses that need to be addressed to meet Cyber Essentials requirements.
CE+ and penetration testing complement each other. Neither is a replacement for the other.
For organisations looking to establish a strong baseline of security, CE+ can provide a structured foundation, while penetration testing can provide deeper insight into how an attacker might compromise the environment.
How MSPs Can Offer CE+ to Their Customers
An MSP does not necessarily need to build its own independent CE+ testing capability.
In fact, maintaining independence is an important consideration when providing certification services.
Instead, an MSP can establish a relationship with an independent security provider.
The MSP can continue to manage the customer's day-to-day technology and remediation, while the security partner performs the independent assessment.
This can provide a straightforward division of responsibilities:
MSP
- Manages the customer's IT environment
- Implements security controls
- Provides remediation
- Maintains systems
- Helps the customer prepare
Independent security provider
- Performs the independent assessment
- Carries out the required technical testing
- Identifies security issues
- Provides assessment results
- Performs appropriate retesting where required
This model can be particularly attractive to MSPs that want to offer CE+ to their customers without employing specialist security testers or developing their own certification infrastructure.
It also allows the MSP to remain focused on what it does best: managing and supporting its customers' technology.
For MSPs looking for an independent CE+ testing partner, the Plainsight Security MSP Partner Programme is designed to provide this type of relationship, allowing MSPs to offer CE+ and security testing services to their customers while retaining their existing customer relationship.
Questions MSPs Should Ask a CE+ Partner
Before choosing a security provider to work with, MSPs should ask some important questions.
Are you an approved CE+ certification body, or do you work with one?
Make sure you understand exactly how the provider delivers the certification and whether the organisation performing the assessment is appropriately authorised within the scheme.
Who performs the technical testing?
Ask about the experience and qualifications of the people carrying out the assessment.
How independent is the assessment?
The value of CE+ comes partly from independent technical verification, so understand how the provider separates assessment from remediation.
Can you work alongside our technical team?
A good security partner should be able to work constructively with the MSP rather than treating the MSP as an obstacle.
How quickly can assessments be scheduled?
This can be particularly important when a customer's certification is linked to a contract, procurement requirement or deadline.
What happens if the customer doesn't pass?
Ask how findings are communicated and what support is available following an unsuccessful assessment.
Do you provide remediation guidance?
While the independent assessor should maintain the appropriate separation from remediation, useful explanations of findings can help the MSP understand what needs to be addressed.
Can you perform retesting?
Understand the provider's approach to reassessment following remediation.
Do you offer partner pricing?
If you intend to provide CE+ to multiple customers, commercial terms can make a significant difference.
Can you support multiple customers?
Consider whether the provider has the capacity to support your customer base as your partnership grows.
What happens when we need an assessment urgently?
An MSP should understand the provider's availability and typical scheduling lead times before an urgent requirement arises.
Making CE+ Part of a Better Security Strategy
Cyber Essentials Plus should not be viewed simply as another certificate to obtain once a year.
For MSPs, it can provide a useful framework around which to build a more consistent approach to customer security.
The MSP helps implement and maintain the controls.
Vulnerability management helps identify emerging weaknesses.
Regular reviews help keep the environment aligned with the requirements.
And independent CE+ testing provides additional assurance that those controls are working as expected.
The result is a much stronger model than preparing for certification at the last minute.
Monitor. Maintain. Review. Remediate. Assess. Repeat.
For customers, the benefit is independent evidence of their security posture.
For MSPs, the benefit is a structured security framework that can complement the services they already provide.
And for both, the ultimate objective is the same: reduce the likelihood that a preventable security weakness becomes a real-world security incident.
Looking for a CE+ Partner?
If you are an MSP looking to offer Cyber Essentials Plus to your customers without building an in-house certification capability, Plainsight Security can work alongside your technical team as an independent security partner.
Our MSP Partner Programme is designed to help MSPs provide access to CE+ assessments and penetration testing while maintaining the customer relationship and continuing to manage remediation themselves.
[Find out more about the Plainsight Security MSP Partner Programme →]

Written by
Mark Tomlinson
Our lead penetration tester, Mark Tomlinson, holds The Cyber Scheme Team Leader qualification in infrastructure penetration testing, an advanced certification recognised by the National Cyber Security Centre (NCSC) and used by professionals testing government systems and UK critical national infrastructure. Mark is also registered with the UK Cyber Security Council as a Principal Cyber Security Professional (PriCSP) specialising in Security Testing and holds an MSc in Computer Science with Cyber Security.
More about how we workPut this into practice.
Cyber Essentials, Cyber Essentials Plus, and penetration testing — fixed-price, plain English, and built to stay out of your way.