
How Long Does Cyber Essentials Certification Take?
A prepared business could achieve Cyber Essentials within days, although security gaps may extend the process to several weeks.
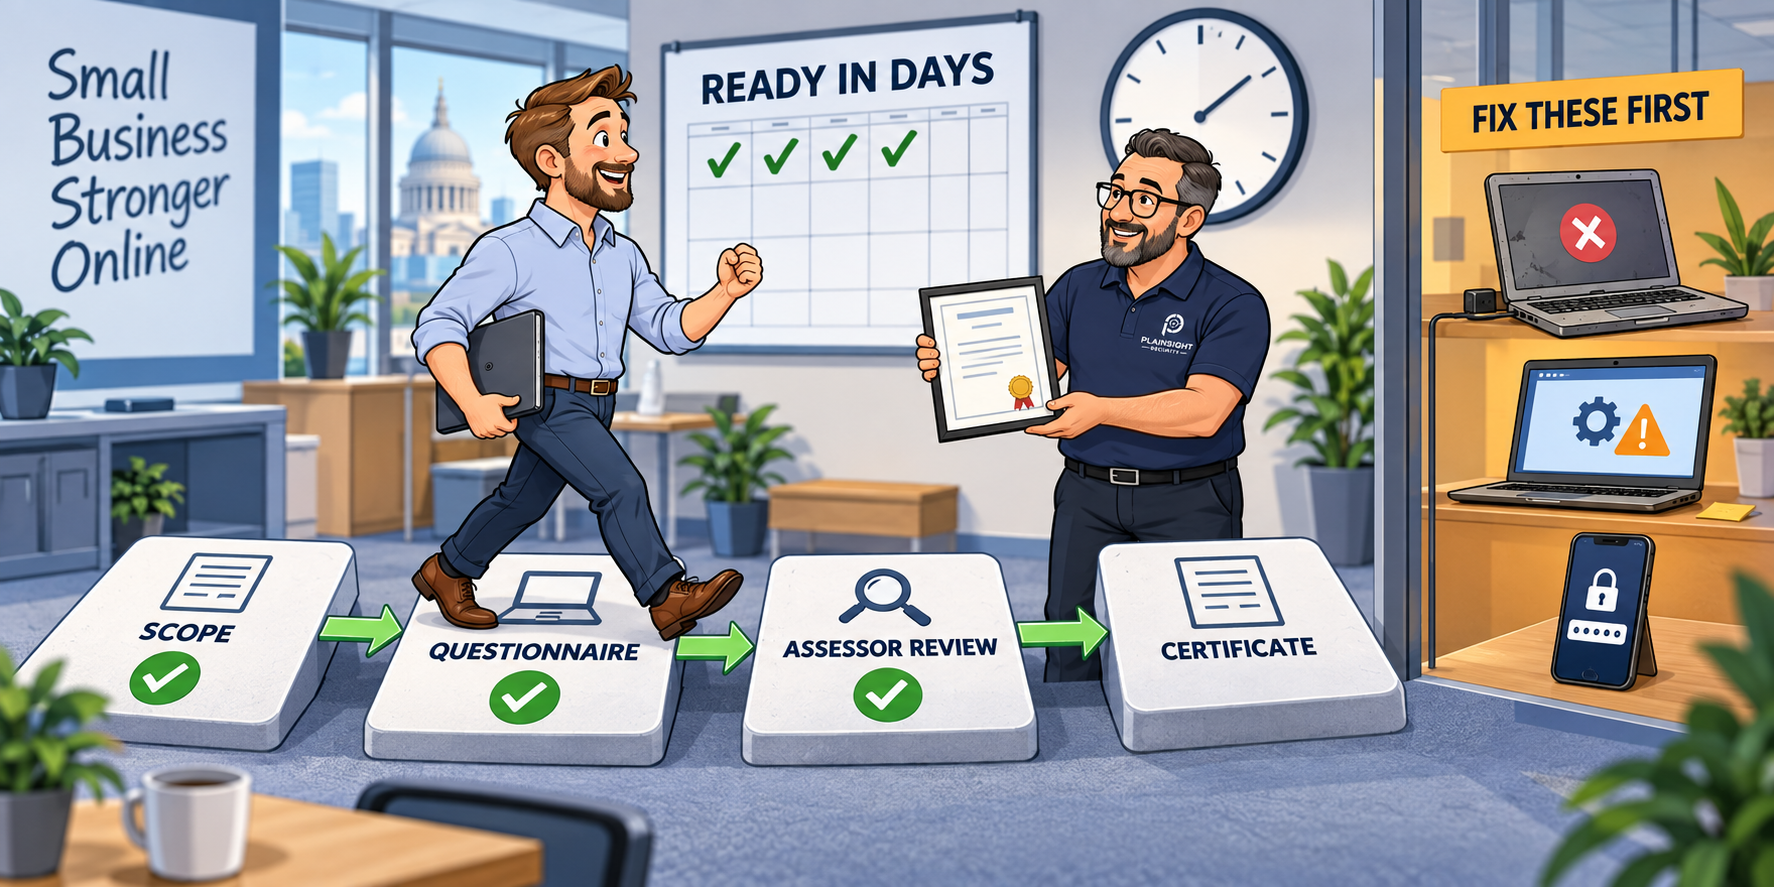
A business that already meets the requirements could achieve Cyber Essentials certification within a few days. If unsupported software, missing security updates, weak authentication or an unclear scope must be addressed first, the process could take several weeks.
Cyber Essentials is a verified self-assessment rather than an on-site technical audit. This means that much of the overall timescale is controlled by the applicant.
Plainsight Security reviews submitted assessments within two working days and can normally issue the certificate on the day the assessment passes.
A typical Cyber Essentials timeline
The following provides an illustration of how long each stage might take:
| Stage | Possible timescale |
|---|---|
| Confirm the organisation and assessment scope | One to two days |
| Collect the required technical information | A few days to several weeks |
| Complete the questionnaire | Several hours to a few days |
| Assessor review by Plainsight Security | Within two working days |
| Clarifications or simple corrections | Up to two working days |
| Certificate issue after passing | Usually the same day |
These are representative timings rather than guarantees. The organisation’s existing security, availability of accurate information and speed of response will have the greatest effect.
What happens during the certification process?
1. Confirm the scope
The first step is to establish exactly what the certification will cover.
This may require identifying:
- Legal entities and trading names
- Office locations
- Internet connections
- Laptops, desktop computers and servers
- Remote workers
- Cloud services
- Mobile and employee-owned devices
- Firewalls and network equipment
- Public IP addresses
A straightforward whole-organisation scope can often be established quickly. Complex corporate structures, separately managed networks and proposed exclusions may require more discussion.
Home workers and personal devices must also be considered if they access organisational data or services. IASME’s guidance on Cyber Essentials scope explains that the assessment covers the devices and services used to access business information.
2. Gather the required information
The applicant needs accurate information about its:
- Operating systems and applications
- Security update processes
- Firewalls and internet routers
- User and administrator accounts
- Password and MFA arrangements
- Malware protection
- Cloud services
- Device estate
This is frequently the longest part of the process.
An organisation with a current asset inventory, centrally managed devices and an engaged IT provider may gather everything within a few days. A business with incomplete records or independently managed equipment may need considerably longer.
3. Complete the questionnaire
The official Cyber Essentials question set can be downloaded and reviewed before purchasing the assessment.
For a small, straightforward organisation with the necessary information available, completing the questionnaire itself may take only a few hours. More complex businesses may need contributions from:
- Internal IT staff
- Managed service providers
- Cloud administrators
- Senior management
- Different offices or departments
Preparing the answers offline before opening the live assessment makes it easier to identify missing information and reduces the risk of rushed or inaccurate responses.
4. Obtain senior approval and submit
A suitably senior person must confirm that the answers are accurate.
This stage should be quick, but submission can be delayed if the appropriate person is unavailable or the technical information has not been properly confirmed.
The person approving the assessment should understand that the answers describe the organisation’s actual controls, not simply what its policies say should happen.
5. Assessor review
A qualified Cyber Essentials assessor reviews the submitted answers against the current certification requirements.
Plainsight Security reviews submitted assessments within two working days. If the answers demonstrate compliance and no clarification is required, the assessment can pass and the certificate can normally be issued that day.
6. Clarifications and corrections
The assessor may request:
- Additional detail
- Confirmation of the scope
- Product names or version information
- An explanation of a security control
- Correction of an apparent misunderstanding
- Clarification of conflicting answers
An unsuccessful initial submission does not necessarily mean starting again. IASME’s current assessment process allows a short period for simple issues to be corrected and the answers resubmitted without another assessment fee.
The resubmission can be made after the first unsuccessful attempt. Substantial technical problems that cannot be corrected in a short time may require a new assessment.
This is why it is better to identify compliance gaps before submitting rather than relying on the correction window.
How long is the assessment available?
Applicants have six months from receiving access to the questionnaire to submit and pass the assessment.
Six months is the maximum assessment window. It does not mean that certification normally takes six months.
If the assessment is not completed successfully within that period, the applicant may need to purchase a new assessment.
Preparing before purchasing helps the organisation use that window effectively and can make certification considerably faster.
What commonly delays Cyber Essentials certification?
An unclear scope
Delays can arise when the organisation is uncertain about:
- Which legal entity is being certified
- Whether particular offices are included
- Which cloud services contain business data
- Whether remote workers and personal devices are in scope
- Who manages specific systems
Scope questions should be resolved before completing the main questionnaire.
Unsupported software
Unsupported operating systems, applications and network devices may need to be:
- Updated
- Replaced
- Removed
- Properly separated from the assessment scope where permitted
Replacing an important business system can take much longer than completing the assessment itself.
Missing security updates
Cyber Essentials requires relevant high-risk and critical security updates to be installed within 14 days of release.
A business with a significant patching backlog may need time to test and deploy updates before it can answer the questionnaire accurately.
Missing multi-factor authentication
MFA is required for cloud services. The organisation may need to identify affected services, adjust licences, configure authentication policies and enrol users. This can extend the timeline if it has not already been completed.
Excessive administrator access
Preparation may identify a need to:
- Create separate administrator accounts
- Remove unnecessary privileges
- Review dormant accounts
- Change working practices
- Document how privileged access is controlled
These changes should be implemented in practice before the assessment is submitted.
Incomplete asset records
A business cannot answer accurately if it does not know which devices, applications and cloud services it uses.
Creating or updating an asset inventory may therefore be one of the most important preparation tasks.
Delayed input from an IT provider
An MSP or external IT provider may hold much of the information needed to complete the assessment.
Involve the provider at the beginning. Waiting until the questionnaire is nearly complete before requesting technical information can cause avoidable delays.
Can Cyber Essentials be completed urgently?
Urgent certification may be possible when:
- The scope is straightforward
- Systems already comply
- Accurate asset information is available
- The appropriate technical contact can respond quickly
- Senior approval is readily available
- Assessor questions are answered promptly
However, businesses should avoid leaving certification until immediately before a tender or customer deadline.
Discovering one unsupported device, unpatched application or missing security control could make an extremely short deadline unrealistic.
If certification is required for a tender, supplier review or insurance renewal, begin the process as soon as the requirement is identified.
How can you achieve certification faster?
- Download and review the current questionnaire before applying.
- Confirm the certification scope.
- Create or update the asset inventory.
- Check operating-system and software support.
- Install outstanding security updates.
- Review user and administrator accounts.
- Enable MFA on cloud services.
- Confirm firewall and router configurations.
- Involve the MSP or internal IT team early.
- Arrange for a senior person to approve the answers.
- Respond promptly to assessor questions.
Preparation usually has a much greater effect on the timescale than the actual process of entering and reviewing the answers.
How long does Cyber Essentials Plus take?
Cyber Essentials Plus takes longer because it adds an independently conducted technical audit.
The timescale depends on:
- Completing Cyber Essentials first
- Assessor availability
- The number and variety of devices
- Availability of staff and sampled equipment
- External and internal testing
- Any technical remediation
- Retesting of failed checks
The Cyber Essentials Plus audit must be completed within three months of achieving the associated Cyber Essentials certification.
A well-prepared organisation may complete the combined process within a few weeks, but the Plus audit must be scoped and scheduled individually.
Frequently asked questions
Can Cyber Essentials be completed in one day?
A fully prepared organisation may be able to complete and submit the questionnaire in one day. The answers must still be reviewed by an assessor, so same-day certification may be possible, but should not be assumed.
How long does the questionnaire take?
A small organisation with the required information may complete it within several hours. Gathering accurate information and resolving security gaps usually takes longer than entering the answers.
How quickly does Plainsight Security review it?
Plainsight Security reviews submitted assessments as soon as possible, but usually within two working days.
What happens if some answers are not compliant?
The assessor will provide feedback. Simple issues may be corrected and the answers resubmitted.
How long is the certificate valid?
Cyber Essentials certification is valid for 12 months from its date of issue. Annual renewal is required to maintain continuous certification.
Should we purchase the assessment before preparing?
Usually not. Download the current question set and assess your readiness first. The six-month assessment window begins when access to the live assessment is provided.
Can Plainsight Security help us complete it more quickly?
Plainsight Security can:
- Clarify the certification scope
- Explain unfamiliar questions
- Identify likely compliance gaps
- Review submitted answers within two working days
- Provide clear feedback where changes are required
- Issue the certificate directly as an IASME-appointed Certification Body
Preparation determines the timescale
The questionnaire and assessor review can be completed relatively quickly. Most delays are caused by gathering information, confirming the scope and correcting technical gaps.
A well-prepared organisation could achieve certification within days. A business that needs to replace unsupported software, apply updates or introduce new security controls should allow several weeks.
Need Cyber Essentials by a particular date?
Tell Plainsight Security what you need and when you need it. We will explain the process, identify any obvious timing risks and help you take the most direct route to certification.

Written by
Mark Tomlinson
Our lead penetration tester, Mark Tomlinson, holds The Cyber Scheme Team Leader qualification in infrastructure penetration testing, an advanced certification recognised by the National Cyber Security Centre (NCSC) and used by professionals testing government systems and UK critical national infrastructure. Mark is also registered with the UK Cyber Security Council as a Principal Cyber Security Professional (PriCSP) specialising in Security Testing and holds an MSc in Computer Science with Cyber Security.
More about how we workPut this into practice.
Cyber Essentials, Cyber Essentials Plus, and penetration testing — fixed-price, plain English, and built to stay out of your way.