
More Than a Certificate: How Cyber Essentials Plus Builds Customer Confidence
Cyber Essentials Plus independently verifies key security controls, helping organisations build trust, support procurement and demonstrate their commitment to cybersecurity.
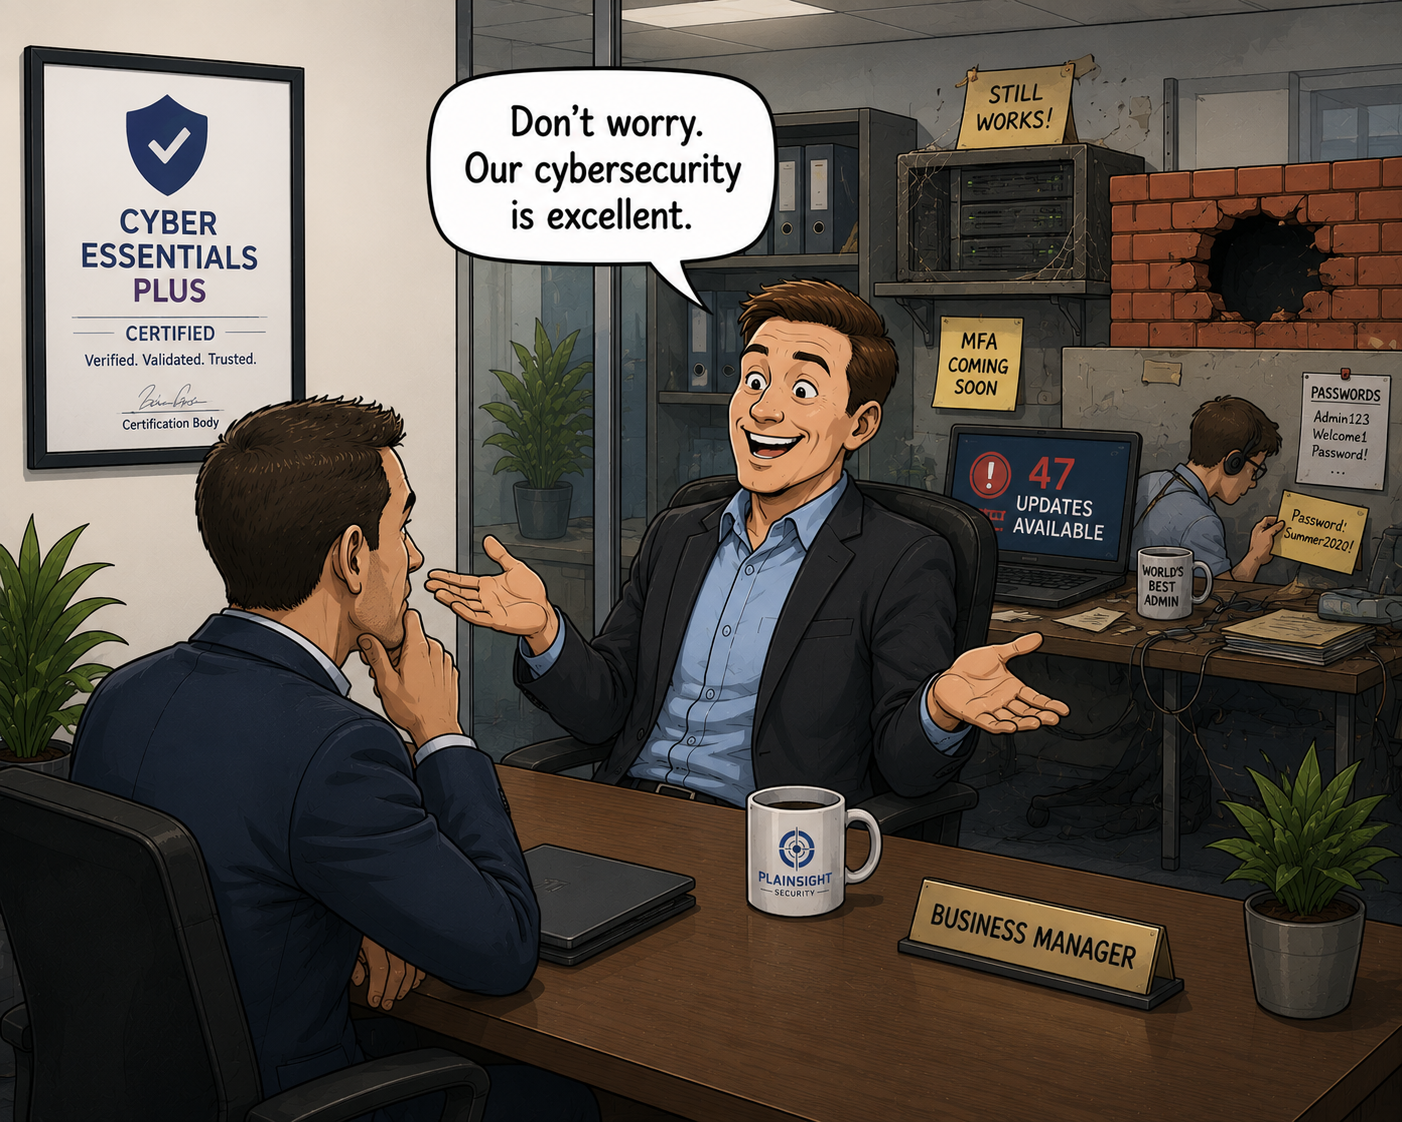
Cybersecurity is no longer something that customers only consider when choosing a large IT supplier.
Businesses of all sizes increasingly rely on third parties for important services. Those suppliers may have access to sensitive information, customer data, Microsoft 365 environments, internal systems, networks, financial information or other business-critical services.
As a result, an organisation's cybersecurity is increasingly becoming part of its customers' own risk management.
This raises an important question:
How can a customer gain confidence that a supplier is taking cybersecurity seriously?
Saying the right things is one thing. Being able to demonstrate that important security controls have been independently assessed is another.
That is where Cyber Essentials Plus can provide real business value.
Customers increasingly care about supplier cybersecurity
Think about the number of organisations your business relies on.
Your IT provider might have access to your systems. Your software providers may process your data. Your accountants, payroll providers, cloud services and other suppliers may all hold information that is important to your organisation.
If one of those suppliers suffers a cyber incident, the consequences may extend beyond their own business.
Depending on the relationship, this could result in:
- Service disruption
- Data exposure
- Operational problems
- Regulatory concerns
- Financial impact
- Reputational damage
It is therefore understandable that customers increasingly want to know how their suppliers approach cybersecurity.
A supplier's cybersecurity can become part of the customer's own security risk.
For that reason, simply saying, "We take cybersecurity seriously", may no longer provide the level of reassurance that customers want.
Saying you are secure is not the same as demonstrating it
Most organisations will tell you that cybersecurity is important to them.
They may have security policies, an IT provider, antivirus or endpoint protection, firewalls and multi-factor authentication.
All of those things can be positive signs.
However, from a customer's perspective, there is an important difference between saying:
"We have these security controls in place."
And being able to say:
"These controls have been independently assessed."
The first is an assurance made by the organisation itself.
The second provides additional evidence.
This is one of the main reasons Cyber Essentials Plus can offer additional value when an organisation wants to demonstrate its approach to cybersecurity to customers, suppliers and other stakeholders.
What does independent verification mean?
Cyber Essentials and Cyber Essentials Plus are both valuable certifications, but they provide assurance in different ways.
Cyber Essentials
Cyber Essentials involves a structured self-assessment that is independently reviewed.
It helps organisations demonstrate that they have important baseline cybersecurity measures in place and have considered how they protect their systems and data.
Cyber Essentials Plus
Cyber Essentials Plus builds on Cyber Essentials by including an independent technical assessment of key security controls.
In simple terms, it moves beyond asking whether certain controls are in place and includes technical verification.
The assessment may include areas relating to:
- Device security
- Security updates
- Malware protection
- User access
- Multi-factor authentication
- Vulnerability assessment
The exact technical assessment is important, but the key business benefit is much simpler to understand.
Cyber Essentials Plus provides independent technical verification of important cybersecurity controls.
That can provide customers with greater confidence than relying solely on an organisation's own declaration that those controls are in place.
For a more detailed explanation of the technical side of the assessment, you can also read our guide to [what Cyber Essentials Plus actually tests].
Why this matters to customers
Put yourself in the customer's position.
Imagine you are choosing between two potential suppliers.
Supplier A says:
"We follow cybersecurity best practices."
Supplier B says:
"Our organisation has achieved Cyber Essentials Plus certification following independent technical assessment."
Neither statement means that the supplier can never suffer a cyber attack.
Cyber Essentials Plus is not a guarantee that an organisation is completely secure, and no sensible cybersecurity professional would claim that it is.
However, the second supplier is able to provide additional evidence that important security controls have been independently assessed.
That can make a difference.
When customers are comparing suppliers, anything that helps them understand and assess cybersecurity risk can make procurement decisions easier.
Supporting supplier security due diligence
Many organisations now carry out some form of security assessment before working with a supplier.
This might involve a supplier-security questionnaire covering areas such as:
- Multi-factor authentication
- Security updates
- Malware protection
- Access control
- Firewalls
- Supported software
- Security policies
- Vulnerability management
These processes can be useful, but they often rely heavily on the supplier's own responses.
Cyber Essentials Plus can provide an additional piece of evidence.
It demonstrates that key baseline controls have been independently assessed rather than simply described by the organisation.
That does not mean Cyber Essentials Plus will replace every supplier-security questionnaire or due-diligence process.
Larger organisations may have specific security requirements depending on the nature of the service being provided and the information involved.
However, CE+ can provide a recognised starting point and reduce the need for customers to rely solely on a supplier's own assurances.
Building trust without asking customers to become cybersecurity experts
This is particularly important for small and medium-sized businesses.
Most customers are not cybersecurity specialists.
They may not have the knowledge or resources to assess things such as:
- Firewall configurations
- Vulnerability management processes
- Multi-factor authentication implementations
- Endpoint security
- Patch management
- Supported software
Nor should every customer have to become a cybersecurity expert simply to gain confidence in a supplier.
An independent certification provides a recognised way of demonstrating that important baseline cybersecurity controls have been assessed.
The customer does not need to personally inspect every device or review every technical configuration.
Instead, they have evidence that an independent assessment has taken place.
That can help make cybersecurity assurance simpler for both sides.
The value for tenders and contracts
Cyber Essentials and Cyber Essentials Plus are also increasingly relevant to organisations bidding for contracts.
Certification may be important when pursuing:
- Public-sector contracts
- Government work
- Framework opportunities
- Larger commercial contracts
- Supply-chain opportunities
In some cases, Cyber Essentials certification may be a specific requirement.
In others, it may not be mandatory but could still help demonstrate that an organisation takes cybersecurity seriously.
Cyber Essentials Plus can demonstrate:
- Commitment to cybersecurity
- Independent verification
- A recognised security baseline
- A proactive approach to reducing cyber risk
This can be particularly valuable during procurement processes.
A potential customer may be comparing several suppliers that offer similar services at similar prices.
Demonstrating independently verified cybersecurity controls could help remove concerns or provide additional reassurance.
Cybersecurity certification can help remove barriers to doing business.
For some organisations, that may be one of the strongest commercial reasons to pursue certification.
Your customers are protecting their own reputation too
Customers are not asking questions about supplier cybersecurity simply to make life more difficult.
They are often protecting themselves.
A cyber incident involving a supplier can have consequences for the customer as well.
Depending on the relationship, a supplier compromise could potentially lead to:
- Service disruption
- Data exposure
- Operational impact
- Regulatory concerns
- Reputational damage
This means customers have a legitimate interest in understanding how their suppliers manage cybersecurity.
Cyber Essentials Plus does not answer every possible security question, but it provides one important piece of evidence.
It shows that an organisation has invested in establishing and independently assessing key cybersecurity controls.
For customers, that can provide additional confidence when making decisions about who they work with.
Particularly valuable for smaller suppliers
Large organisations may have dedicated security teams, security operations centres, external audits, ISO 27001 certification and complex assurance programmes.
Most smaller organisations do not.
That does not mean they cannot demonstrate that they take cybersecurity seriously.
In fact, this is one area where Cyber Essentials Plus can be particularly valuable.
It provides a recognised and accessible way for smaller organisations to demonstrate that key technical security controls have been independently assessed.
A small business may not have a Chief Information Security Officer or a dedicated team of cybersecurity professionals.
But it can still take meaningful steps to protect its systems and demonstrate those efforts to customers.
Cyber Essentials Plus can help provide that evidence.
For SMEs looking to work with larger customers, join supply chains or compete for new contracts, this can be particularly important.
The certificate is not the only benefit
It is easy to focus entirely on achieving the certificate.
However, the certification itself is only part of the value.
Preparing for Cyber Essentials Plus and undergoing the assessment can identify issues that need attention.
These might include:
- Missing security updates
- Unsupported software
- Configuration problems
- Weaknesses in security controls
- Vulnerabilities requiring remediation
The real value is not simply being able to say:
"We got the certificate."
It is also being able to say:
"We independently assessed important security controls and addressed the issues we found."
That makes Cyber Essentials Plus more than a compliance exercise.
It can also support genuine security improvement.
Ideally, the assessment should not be viewed as a one-off event that is forgotten as soon as the certificate arrives.
The findings and lessons from the process can help an organisation strengthen its cybersecurity practices going forward.
Using Cyber Essentials Plus in customer conversations
Once an organisation has achieved Cyber Essentials Plus, the certification can become part of its wider customer and business conversations.
It can be referenced appropriately in:
- Tender responses
- Supplier questionnaires
- Procurement discussions
- Company websites
- Sales proposals
- Customer communications
However, it is important to communicate certification accurately.
The message should not be:
"We are completely secure."
No cybersecurity certification can honestly support that claim.
A more accurate and credible message would be:
"We have achieved Cyber Essentials Plus, providing independent technical verification of key cybersecurity controls."
That communicates the real value without making unrealistic promises.
It demonstrates that the organisation has invested in cybersecurity and has taken the additional step of having important controls independently assessed.
Certification does not mean risk disappears
It is important to be realistic about what Cyber Essentials Plus does and does not mean.
Achieving CE+ does not mean:
- You can never be hacked
- Every vulnerability has been eliminated
- Every employee will recognise every phishing attempt
- Every supplier you work with is secure
- Every security control will remain correctly configured forever
Cybersecurity requires ongoing effort.
Systems change. New vulnerabilities are discovered. Employees join and leave. Software is updated. Threats evolve.
Maintaining good cybersecurity requires continued attention.
However, Cyber Essentials Plus can provide evidence that an organisation has achieved and independently verified an important security baseline.
That is valuable, even though it is not a guarantee against every possible cyber threat.
Why independent verification matters
Ultimately, the value of Cyber Essentials Plus comes back to one simple point.
There is a fundamental difference between:
Trust us
And:
We can demonstrate it
Many organisations genuinely take cybersecurity seriously.
But customers are increasingly looking for evidence.
Cyber Essentials Plus helps organisations provide some of that evidence by demonstrating that key cybersecurity controls have been independently and technically assessed.
For customers, that can provide additional confidence.
For suppliers, it provides a recognised way to demonstrate their commitment to cybersecurity.
For both sides, it can make cybersecurity assurance more straightforward.
More than a certificate
Customers increasingly need confidence that the organisations they work with take cybersecurity seriously.
Cyber Essentials Plus provides more than a certificate to display on a website.
It provides independent technical verification of key cybersecurity controls, helping organisations demonstrate that they have invested in establishing and assessing an important security baseline.
It does not guarantee that an organisation will never suffer a cyber attack.
But it can provide customers with something more meaningful than a simple promise that cybersecurity is being taken seriously.
For businesses, particularly smaller organisations looking to build trust, win contracts and meet customer expectations, that independent verification can be valuable.
In a world where supplier cybersecurity increasingly matters, being able to demonstrate your commitment to security can help build customer confidence.

Written by
Mark Tomlinson
Our lead penetration tester, Mark Tomlinson, holds The Cyber Scheme Team Leader qualification in infrastructure penetration testing, an advanced certification recognised by the National Cyber Security Centre (NCSC) and used by professionals testing government systems and UK critical national infrastructure. Mark is also registered with the UK Cyber Security Council as a Principal Cyber Security Professional (PriCSP) specialising in Security Testing and holds an MSc in Computer Science with Cyber Security.
More about how we workPut this into practice.
Cyber Essentials, Cyber Essentials Plus, and penetration testing — fixed-price, plain English, and built to stay out of your way.