
Penetration test vs vulnerability scan: what is the difference?
A scan and a pentest are not the same thing, and the gap between them is where real breaches happen. Here is what each one does, and when you need which.
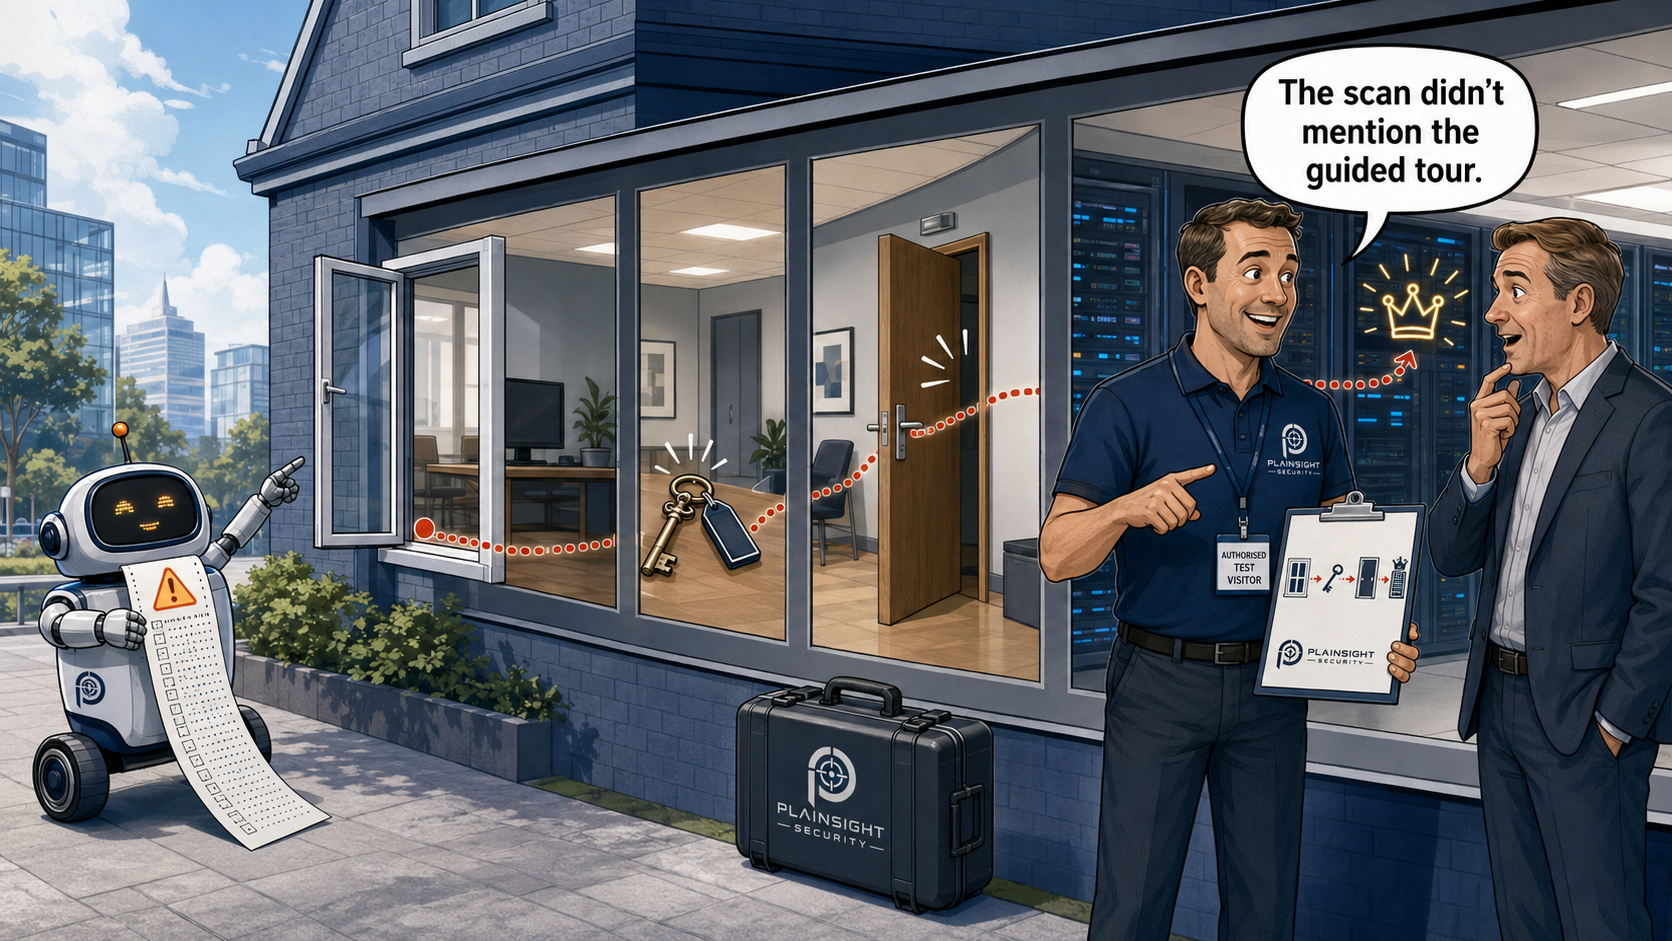
"We had a scan done, aren't we covered?" It is a fair question, and the answer matters, because a vulnerability scan and a penetration test are genuinely different things. The gap between them is exactly where real breaches tend to live.
What a vulnerability scan does
A vulnerability scan is automated. A tool checks your systems against a database of known issues — missing patches, weak configurations, outdated software — and produces a list, usually ranked by severity.
Scans are fast, affordable and genuinely useful. Run regularly, they are a great way to keep on top of known problems at scale. But an automated tool has real limits:
- It reports issues in isolation, and cannot tell that two "medium" findings chain together into a full compromise.
- It does not understand your business logic — that this user should not be able to reach that data.
- It generates false positives and lacks the judgement to know which findings actually matter in your environment.
A scanner tells you what *might* be wrong. That is valuable, but it is not the whole picture.
What a penetration test does
A penetration test is a person. An experienced tester examines your environment by hand, thinks like an attacker, and chains findings together the way a real adversary would — then safely demonstrates genuine impact where a way in exists.
The output is not just a list. It is a clear account of what an attacker could actually achieve, which issues to fix first, and reproduction steps your team can follow. Crucially, a good tester reasons about *intent* and *context*: the exact things automation cannot do.
A scanner finds the unlocked window. A tester climbs through it, moves through the house, and shows you what is actually at risk.
So which do you need?
Both, ideally — they answer different questions. Regular scanning keeps you on top of known, published issues between engagements. Periodic penetration testing finds the deeper problems: logic flaws, chained weaknesses, and the exposures automation simply cannot reason about.
The mistake to avoid is buying one and believing you have the other. A scan is not a pentest, and a compliance tick-box that only requires a scan will not surface the issues that lead to the worst incidents.
How we test
Our infrastructure testing — external and internal — is hands-on and methodology-led, delivered by a tester who holds The Cyber Scheme's Team Leader infrastructure qualification (CSTL-INF), one of the certifications recognised by the NCSC against UK government standards. Web application testing follows the OWASP standards, with authenticated, role-aware testing that finds the logic flaws a scanner never will.
If you want to know what a real attacker could do — not just what a tool flags — get a fixed-price quote and we will scope the right test for your environment, not the biggest one.
How much does penetration testing cost?
The cost of a penetration test depends on what you need tested, the size and complexity of the environment, and the depth of testing required. There is no meaningful one-size-fits-all price for a properly scoped penetration test.
Factors that can affect the cost include:
- Scope: the number of applications, systems, IP addresses or environments being tested
- Complexity: custom applications, APIs, authentication and business logic can require additional testing
- Type of test: web application, API, external and internal penetration tests all require different approaches
- Testing depth: the level of access and information provided to the tester can affect the time required
- Reporting: detailed technical findings and remediation guidance form an important part of a professional penetration test
- Retesting: you may wish to have vulnerabilities reassessed after remediation
A penetration test should not be priced simply by the number of systems being tested. The objective is to provide meaningful assurance that vulnerabilities have been identified and properly investigated, rather than simply generating as many findings as possible.
At Plainsight Security, we discuss your requirements first, agree an appropriate scope and then provide a clear, fixed-price quotation for the work.
Not sure what type of penetration test you need? That's fine. Tell us what you're trying to achieve and we'll help you determine the most appropriate approach.

Written by
Mark Tomlinson
Our lead penetration tester, Mark Tomlinson, holds The Cyber Scheme Team Leader qualification in infrastructure penetration testing, an advanced certification recognised by the National Cyber Security Centre (NCSC) and used by professionals testing government systems and UK critical national infrastructure. Mark is also registered with the UK Cyber Security Council as a Principal Cyber Security Professional (PriCSP) specialising in Security Testing and holds an MSc in Computer Science with Cyber Security.
More about how we workPut this into practice.
Cyber Essentials, Cyber Essentials Plus, and penetration testing — fixed-price, plain English, and built to stay out of your way.