 Web Application Security
3 Sep 2026 · 17 min read
Weak API authentication can allow attackers to bypass login controls, MFA and session protections. Manual testing helps uncover these hidden weaknesses.
Read the article →
 Web Application Security
29 Aug 2026 · 16 min read
Authentication testing examines login, MFA, password recovery, APIs and session handling to identify practical routes attackers could use to compromise user accounts.
Read the article →
 Web Application Security
29 Aug 2026 · 16 min read
Small configuration mistakes can expose sensitive data, administrative functions and wider application infrastructure.
Read the article →
 Web Application Security
29 Aug 2026 · 16 min read
MFA is highly effective, but weak workflows, recovery routes, APIs or session handling can create ways around it.
Read the article →
 Web Application Security
29 Aug 2026 · 15 min read
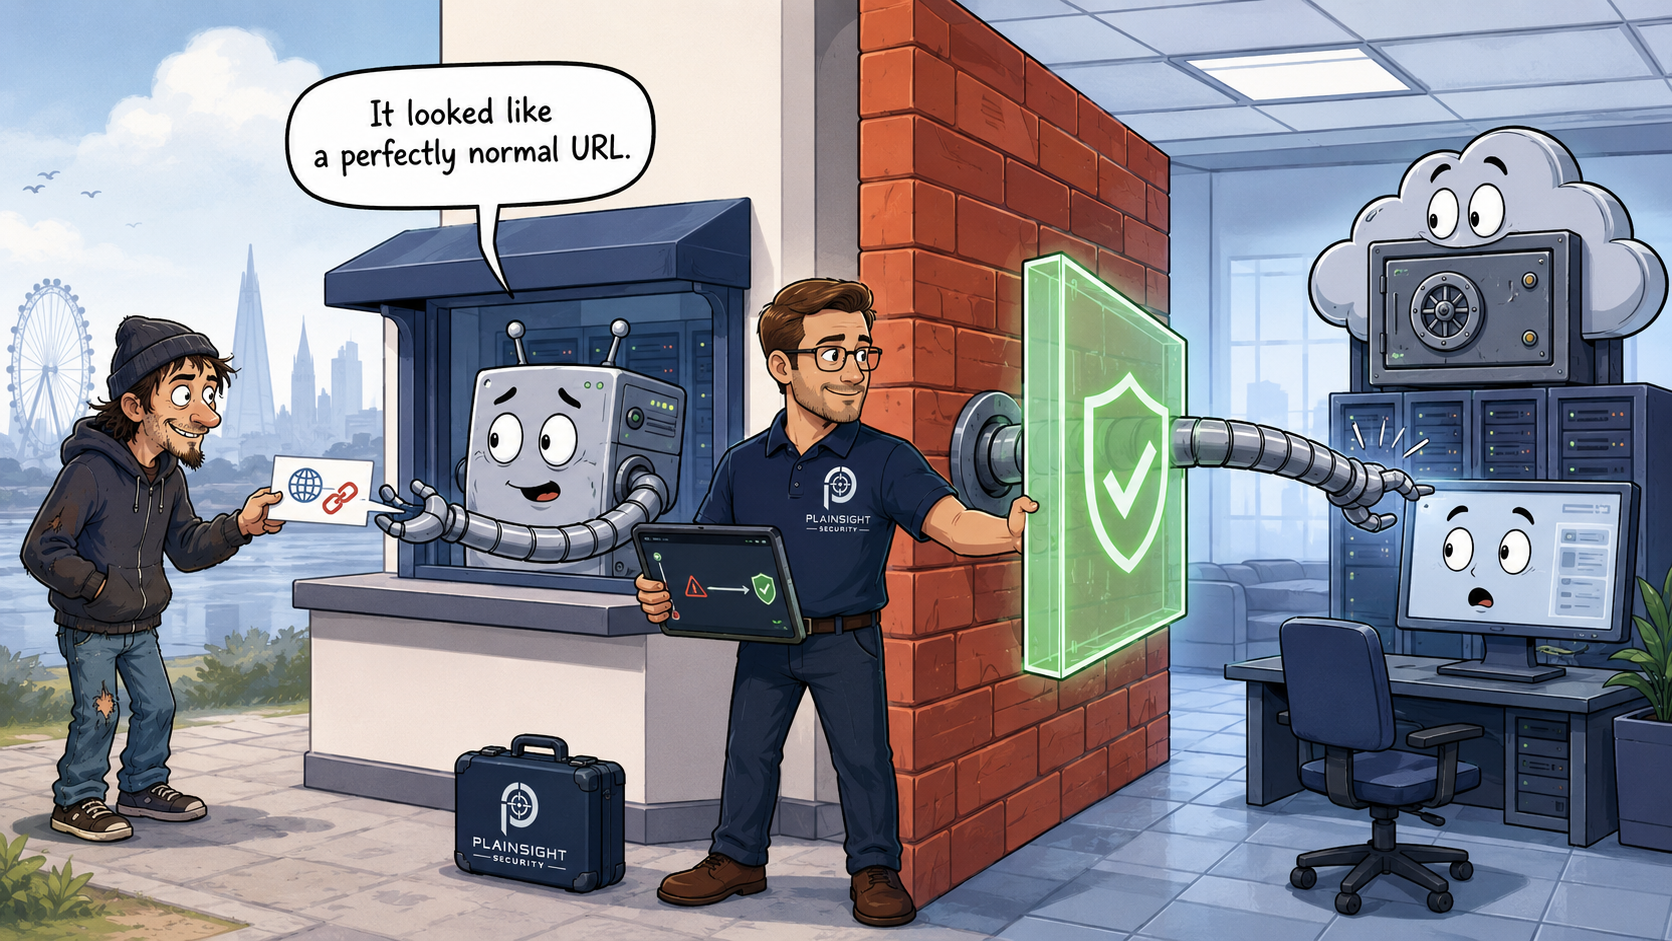
SSRF can trick a web application into accessing internal systems, cloud services and sensitive resources on an attacker’s behalf.
Read the article →
 Web Application Security
23 Aug 2026 · 11 min read
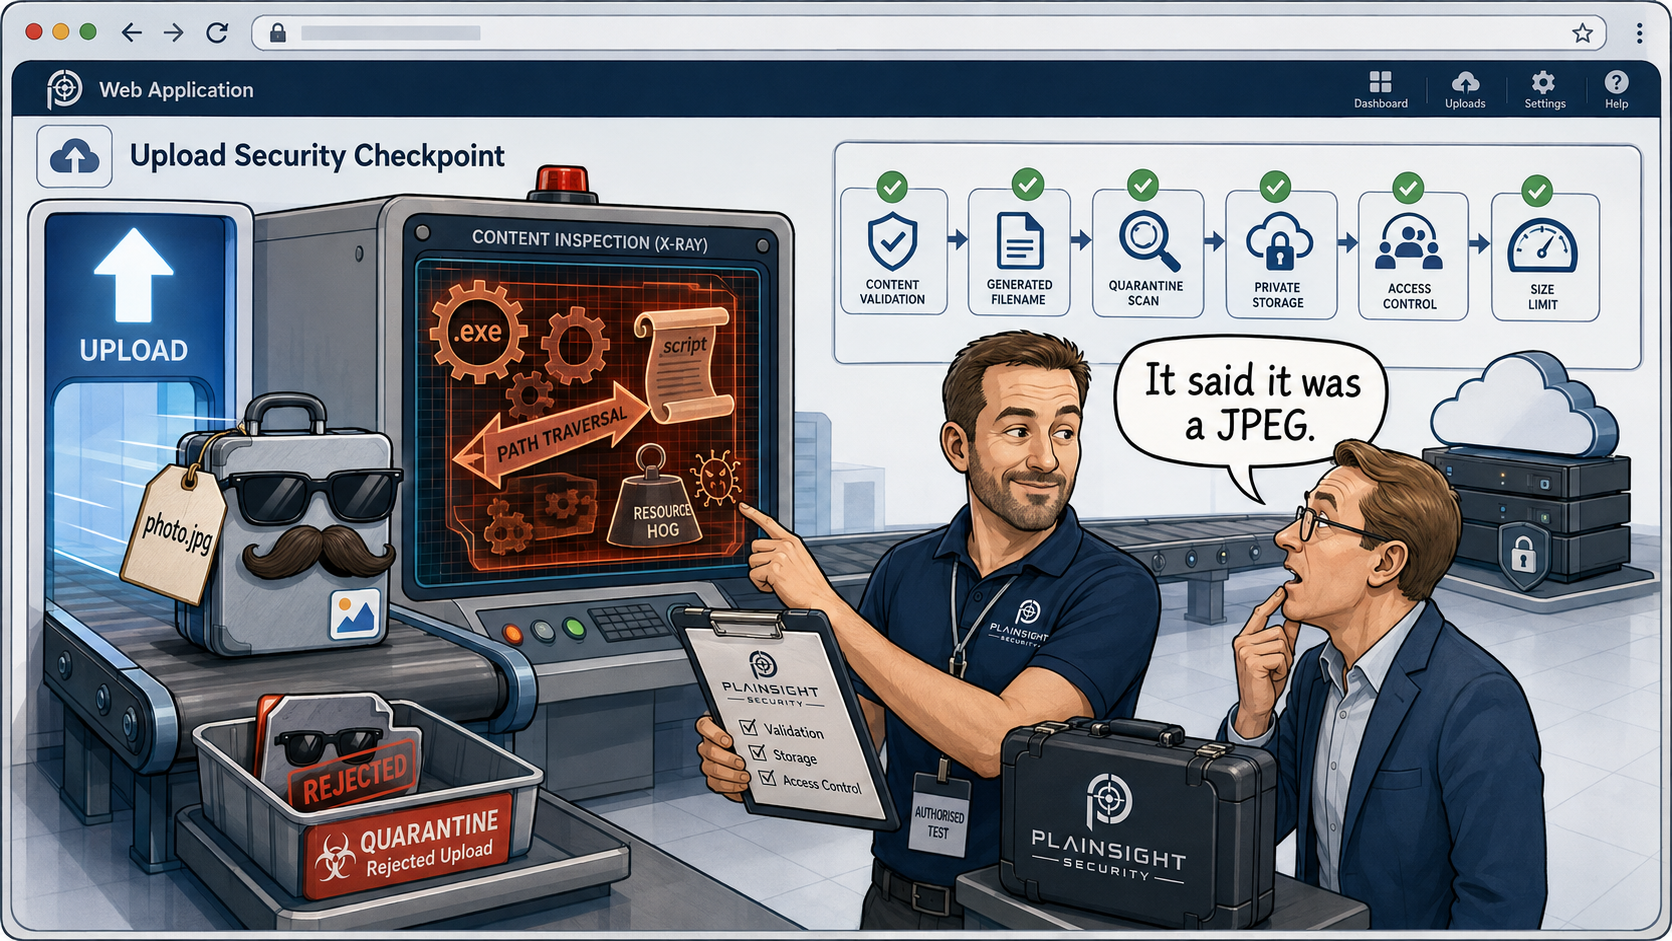
File uploads are a common but often overlooked web application attack surface. This article explains how insecure upload handling can lead to data exposure, malware distribution, denial of service and potentially code execution.
Read the article →
 Web Application Security
22 Aug 2026 · 6 min read
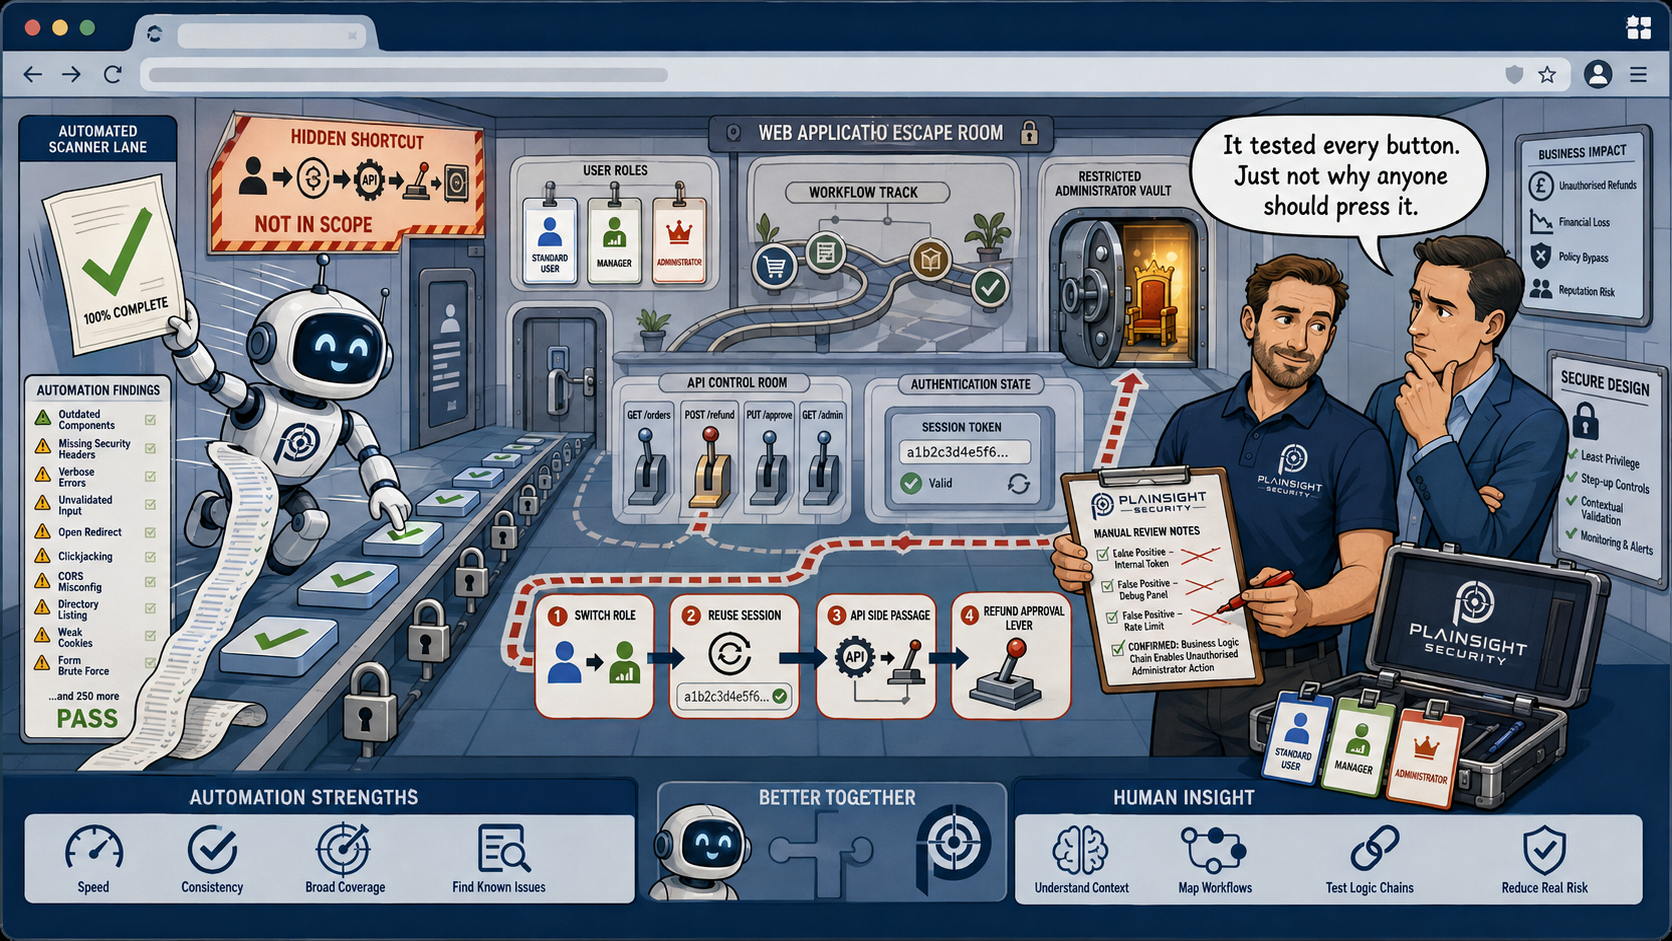
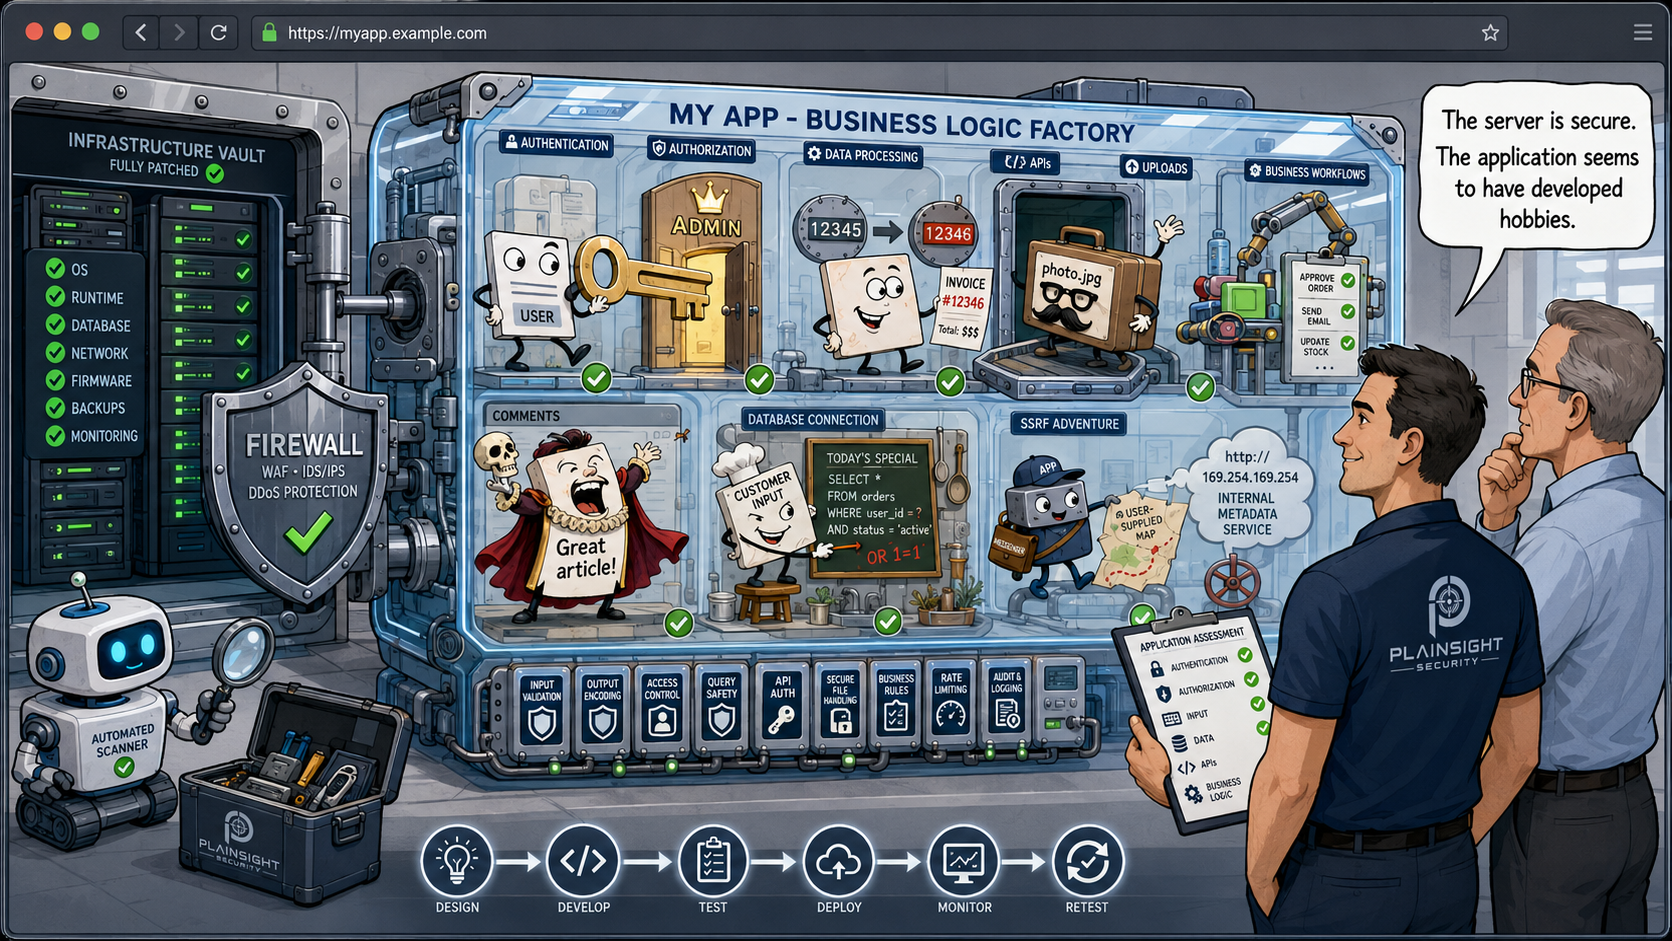
Automated scanners miss access-control, authentication and business-logic flaws. Learn why web applications also need manual penetration testing.
Read the article →
 Web Application Security
22 Aug 2026 · 7 min read
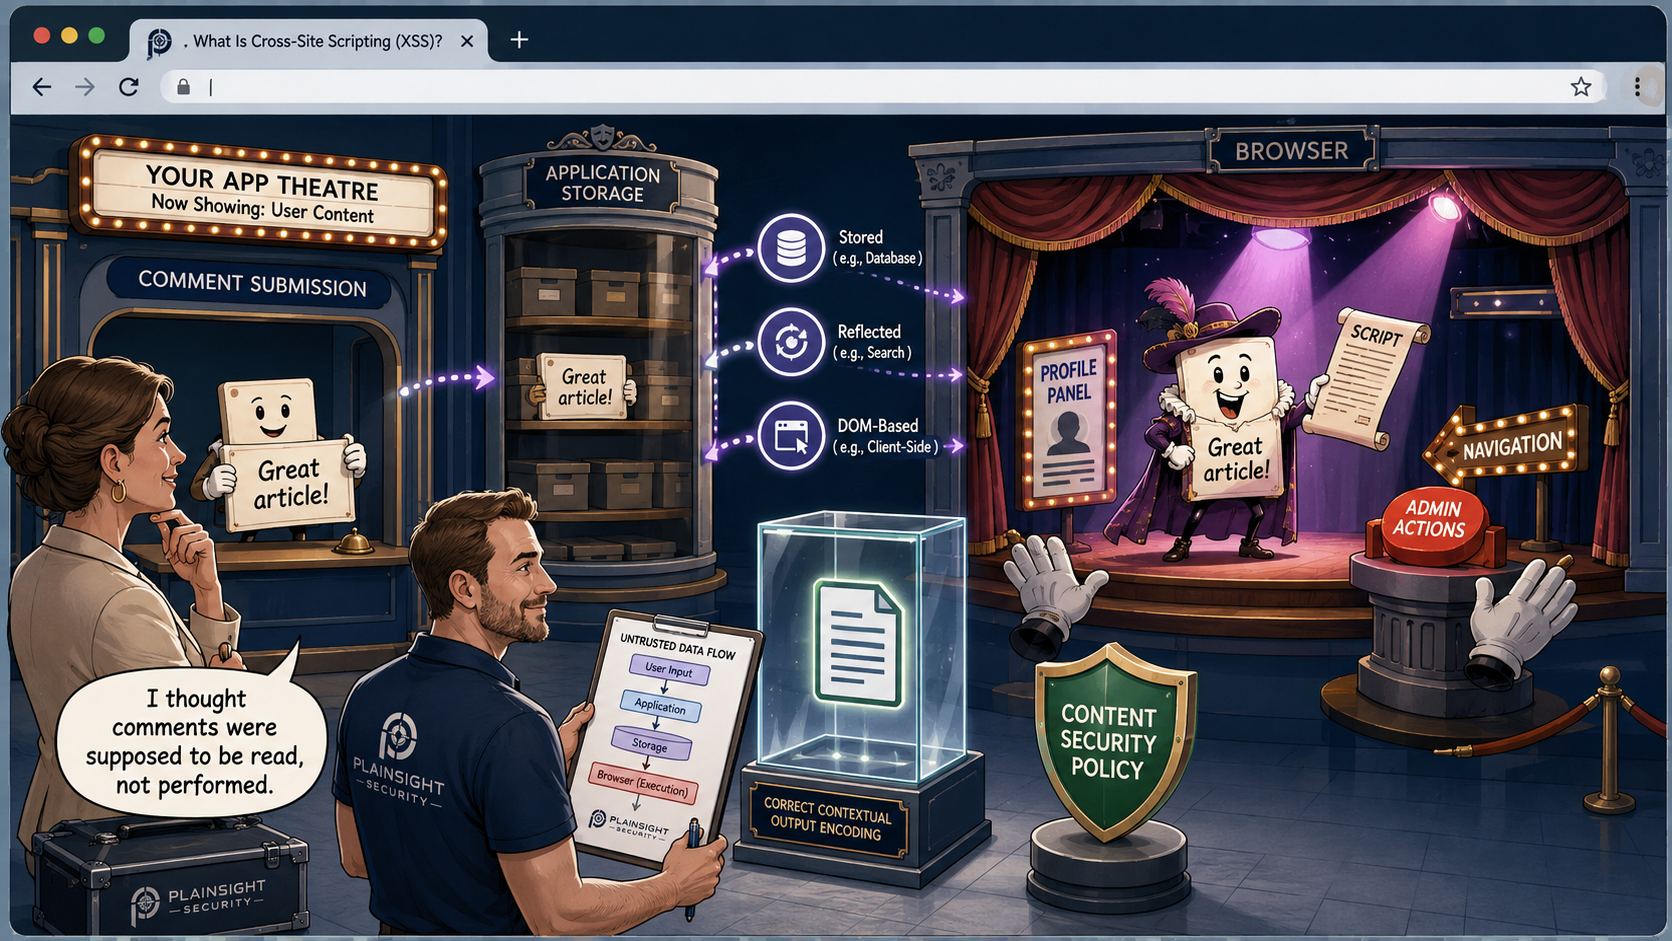
An overview of Cross-Site Scripting (XSS), how attackers can inject malicious content into web applications, the risks involved, and how organisations can prevent it.
Read the article →
 Web Application Security
22 Aug 2026 · 6 min read
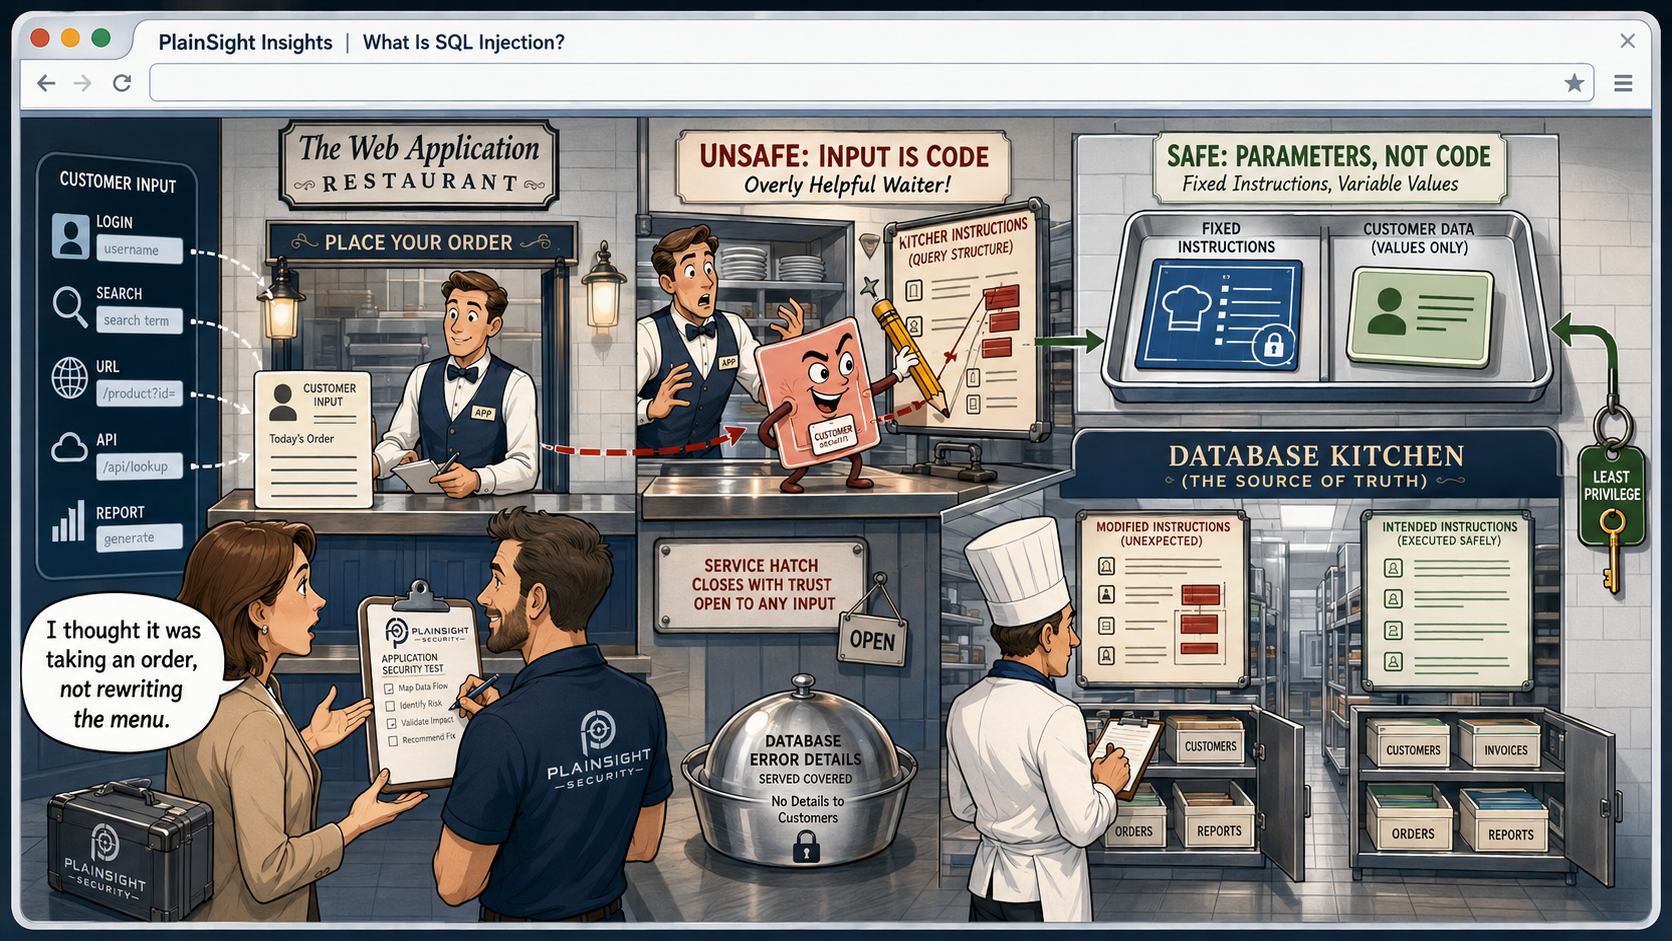
An overview of SQL injection, how attackers can manipulate database queries, the risks involved, and the key measures organisations can use to prevent it.
Read the article →
 Web Application Security
20 Aug 2026 · 6 min read
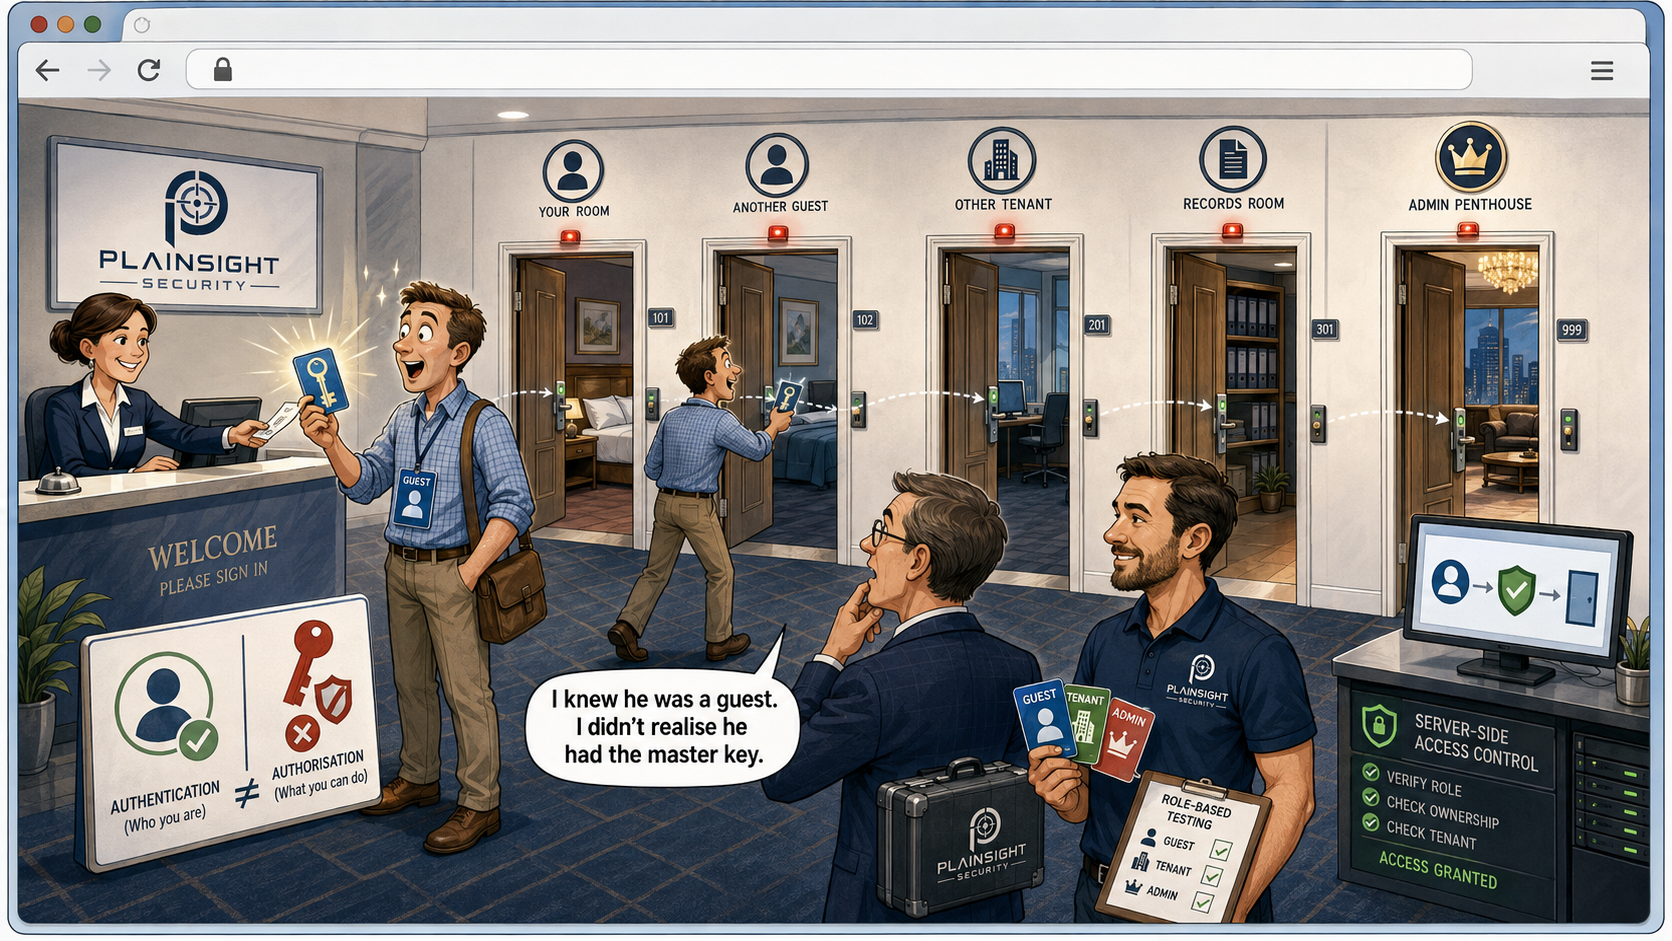
Broken access control can expose sensitive data and restricted functions. Learn how penetration testing identifies exploitable authorisation flaws.
Read the article →
 Web Application Security
20 Aug 2026 · 11 min read
A practical guide to web application risks, scanning limitations and how manual penetration testing helps protect applications and customer data.
Read the article →
 Web Application Security
20 Aug 2026 · 6 min read
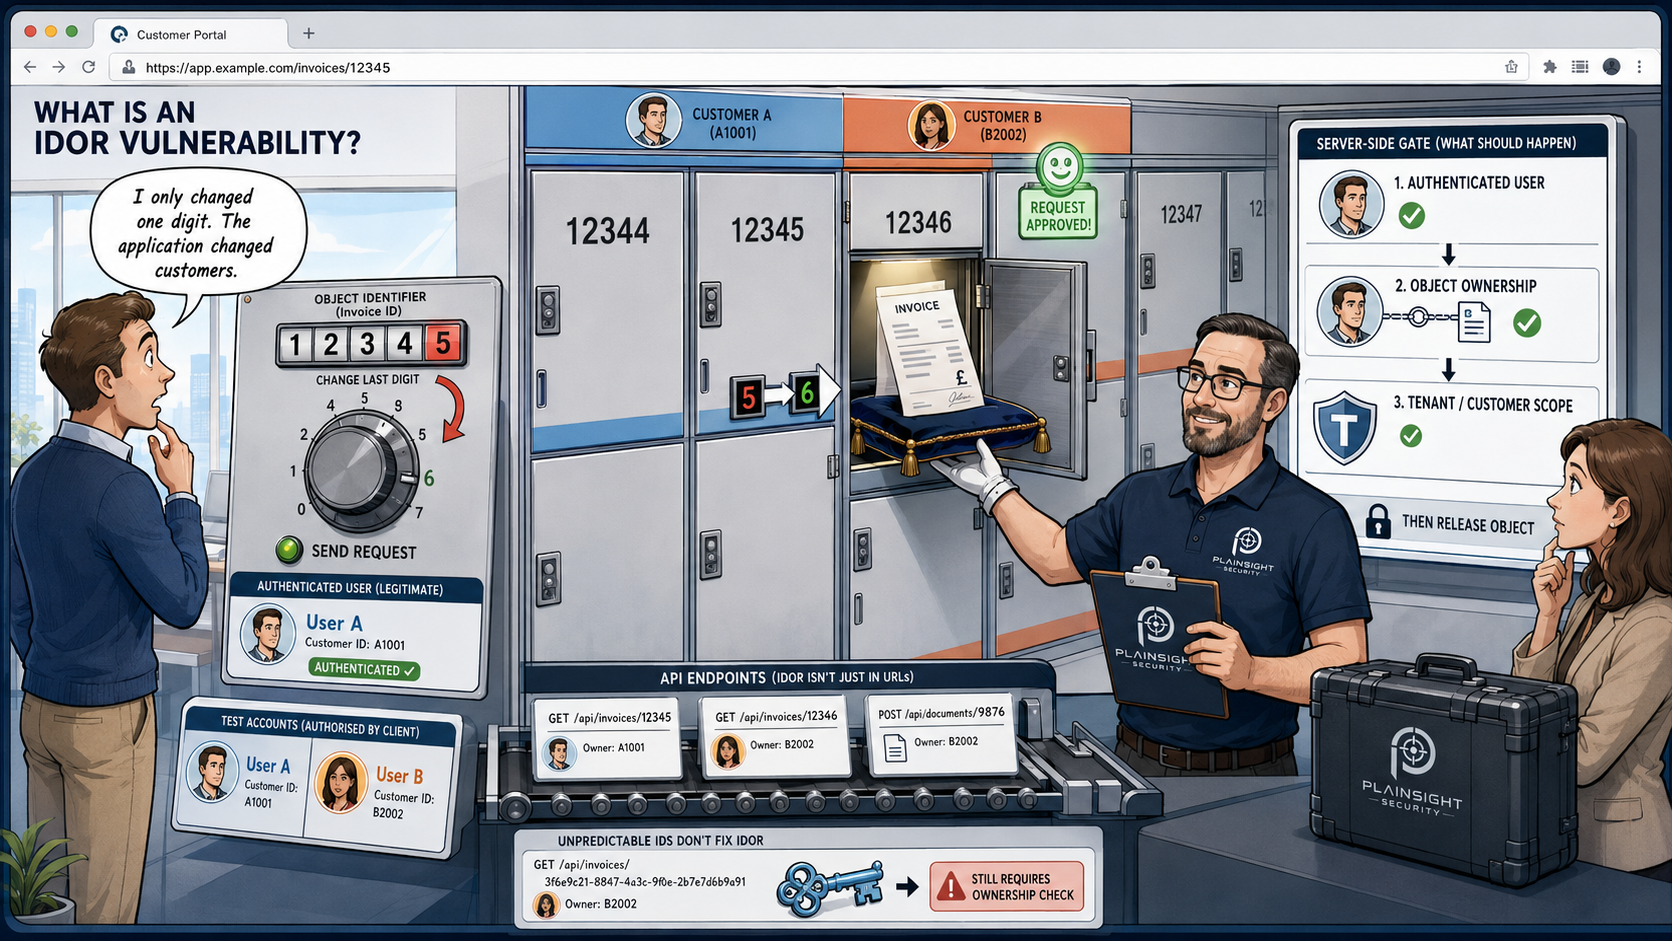
An overview of IDOR vulnerabilities, how attackers can bypass access controls to access other users' data, and how organisations can identify and prevent them.
Read the article →
